Vulnerability
[FAIL] Unrestricted Resource Consumption - Authentication - Login Rate Limiting
Description
The crAPI login endpoint applies neither rate limiting nor account lockout. Repeated failed login attempts are not limited, enabling brute force/credential stuffing and unbounded consumption of server resources.
Impact
Availability: the server can be flooded with authentication requests without restriction. Confidentiality: enables credential brute force to take over accounts.
CWE
CWE-307: Improper Restriction of Excessive Authentication Attempts (CWE-770: Allocation of Resources Without Limits)
OWASP
API4:2023 - Unrestricted Resource Consumption
Scenario
Normal: a single failed login -> 401. Exploitation: 20 consecutive attempts -> all 401 with no 429/lockout, proving there is no restriction.
Endpoint
POST http://127.0.0.1:8888/identity/api/auth/login
Affected feature
Login Authentication (crapi-identity)
Remediation
- Apply per-account/IP rate limiting and progressive account lockout.
- Add CAPTCHA/anti-automation and anomaly detection.
- Limit concurrency/requests per client.
Proof of concept
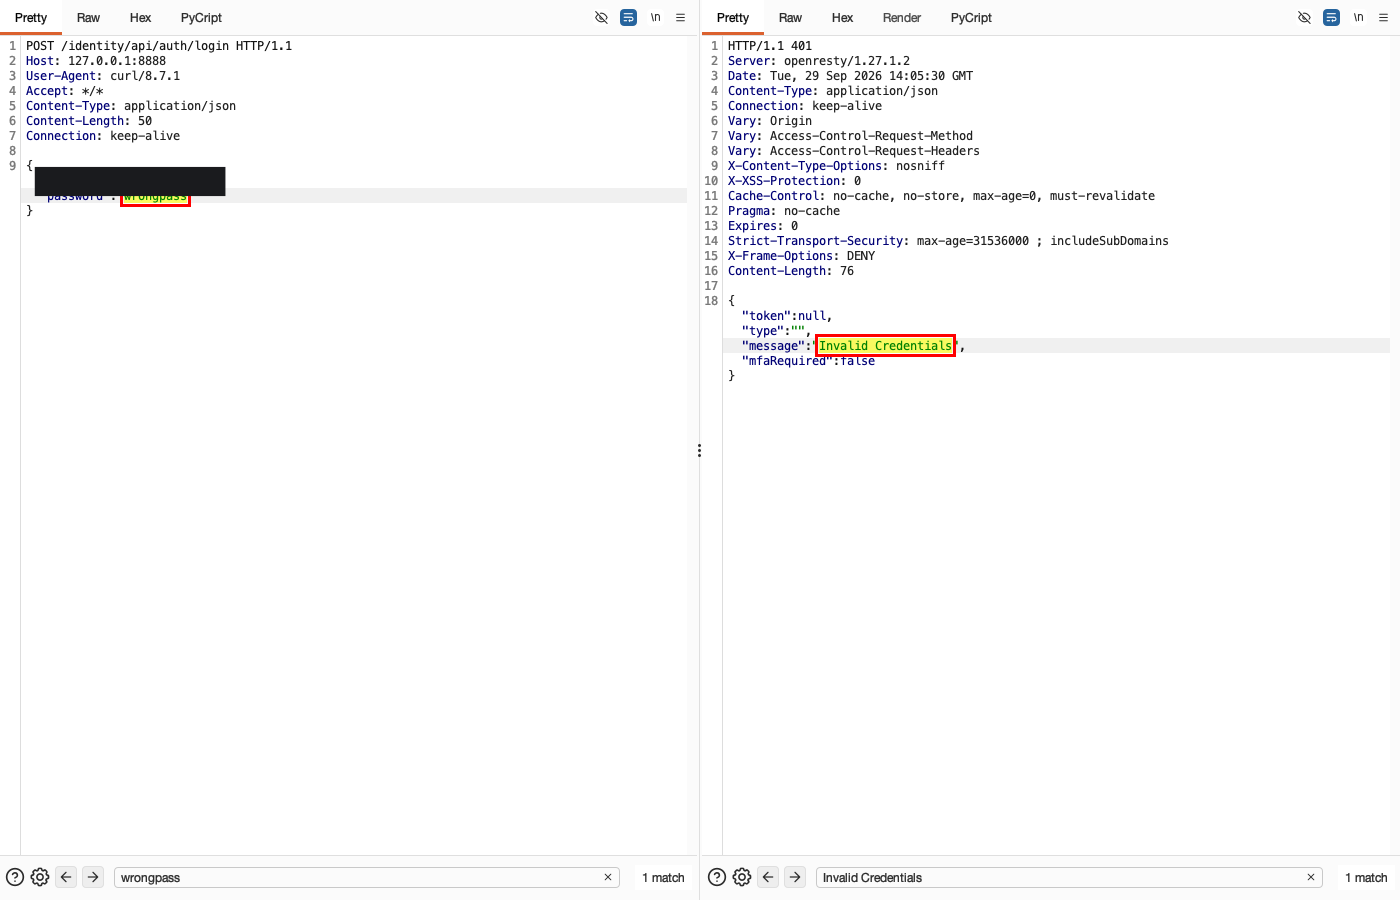
- (Screenshot 1) NORMAL: POST /identity/api/auth/login with a wrong password -> 401.
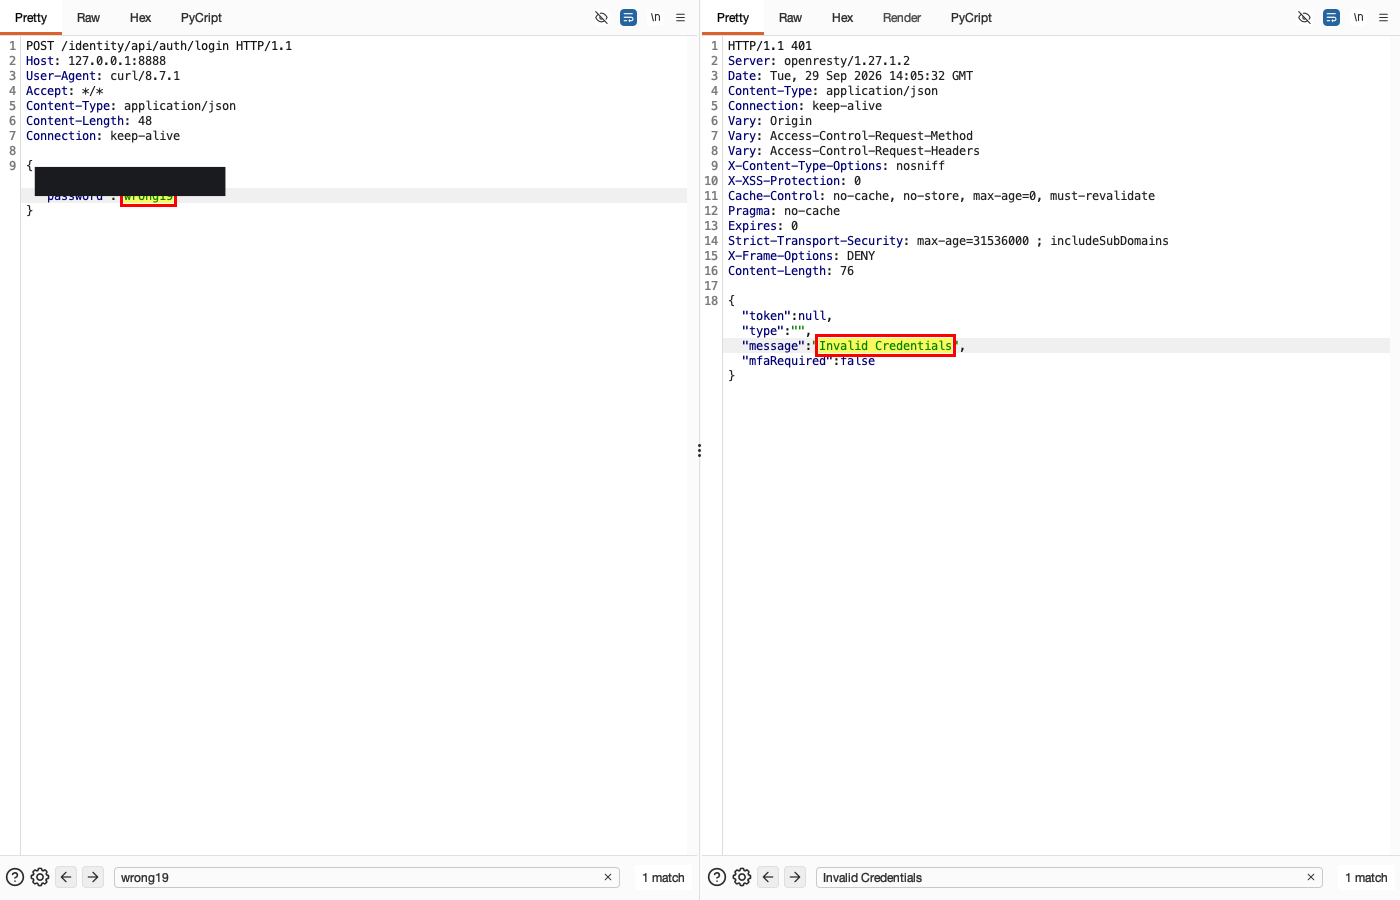
- (Screenshot 2) EXPLOITATION: send 20 consecutive login attempts -> all 401 with no HTTP 429/lockout, proving there is no rate limiting.
The complete record
LAB All targets are lab systems. Nothing here is a client engagement. Evidence is shown as recorded; secrets are blacked out.
Normal: one failed login
Normal flow: one login attempt with an incorrect password returns 401.
HTTP request
POST /identity/api/auth/login HTTP/1.1
Host: 127.0.0.1:8888
Content-Type: application/json

{"email":"[REDACTED-EMAIL]","password":"[REDACTED-LAB-VALUE]"}
HTTP response
HTTP/1.1 401
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 76

{
  "token": null,
  "type": "",
  "message": "Invalid Credentials",
  "mfaRequired": false
}
Observation: 20 login attempts, no rate limit
Impact: the 20 login attempts encounter no rate limit. This leaves the login exposed to credential brute-force, credential stuffing and unrestricted resource consumption, putting availability and confidentiality at risk. The capture does not demonstrate account takeover or denial of service.
HTTP request
POST /identity/api/auth/login HTTP/1.1
Host: 127.0.0.1:8888
Content-Type: application/json

{"email":"[REDACTED-EMAIL]","password":"[REDACTED-LAB-VALUE]"}
# 20 percobaan login BERUNTUN -> semua 401, TIDAK ada HTTP 429/lockout
HTTP response
Status 20 percobaan beruntun:
401 401 401 401 401 401 401 401 401 401 401 401 401 401 401 401 401 401 401 401

=> tidak ada 429/lockout pada percobaan mana pun.
← Previous case: Unrestricted Access to Sensitive Business Flow - Shop - Coupon Claim Next case: Unsafe Consumption of APIs - Workshop - Contact Mechanic Upstream →