Vulnerability
[PASS] NoSQL Injection - Community - Coupon Validation (Normal Input)
Description
Tested coupon validation with ordinary string input (valid and unknown), without NoSQL operators.
Impact
No impact: valid codes are accepted and unknown codes are rejected as expected.
CWE
CWE-943: NoSQL Injection (negative test for ordinary string input)
OWASP
API8:2023 - Security Misconfiguration (negative test - normal input)
Scenario
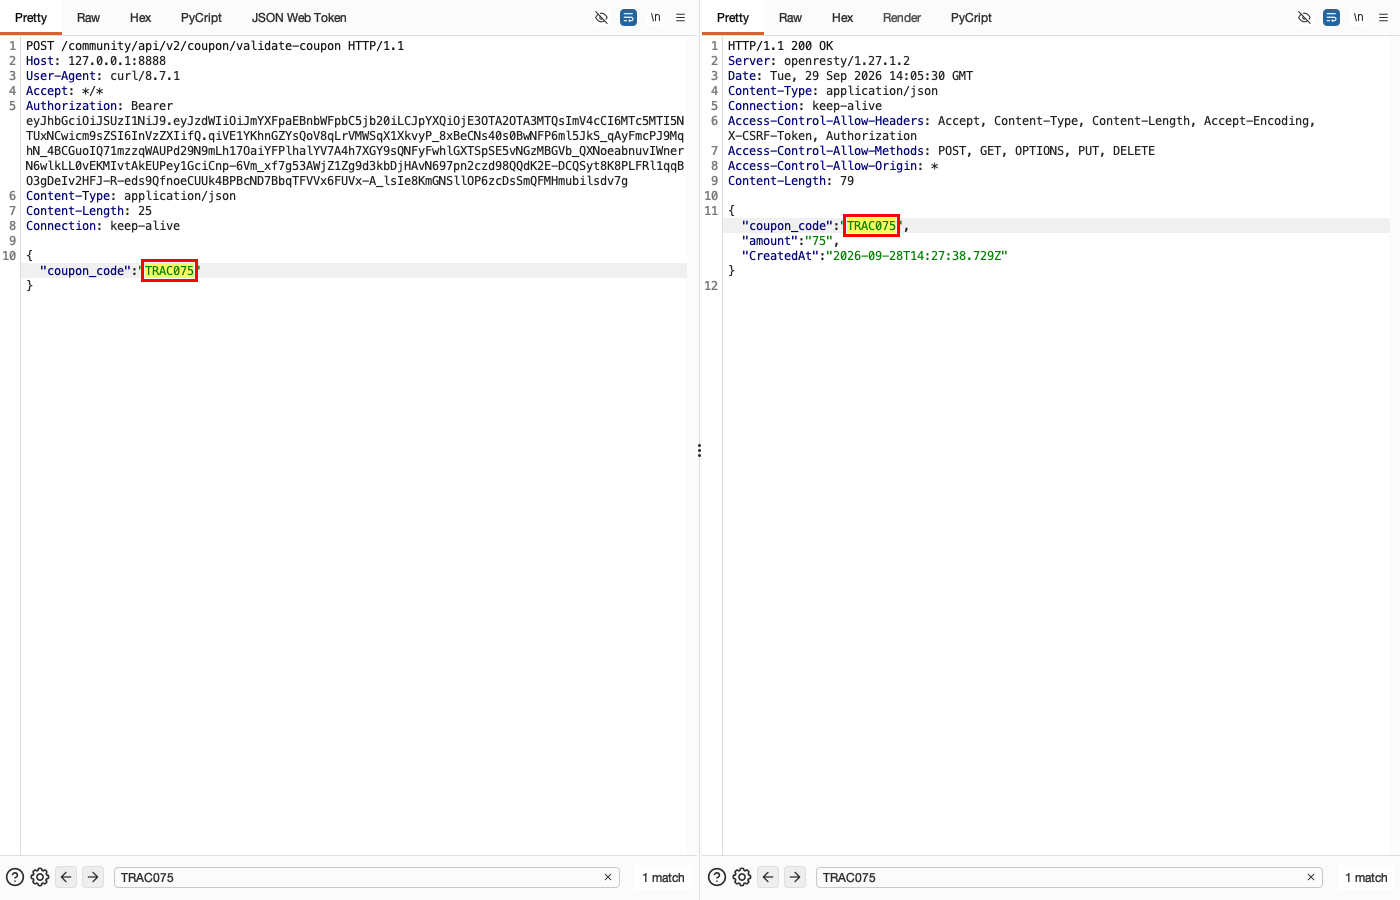
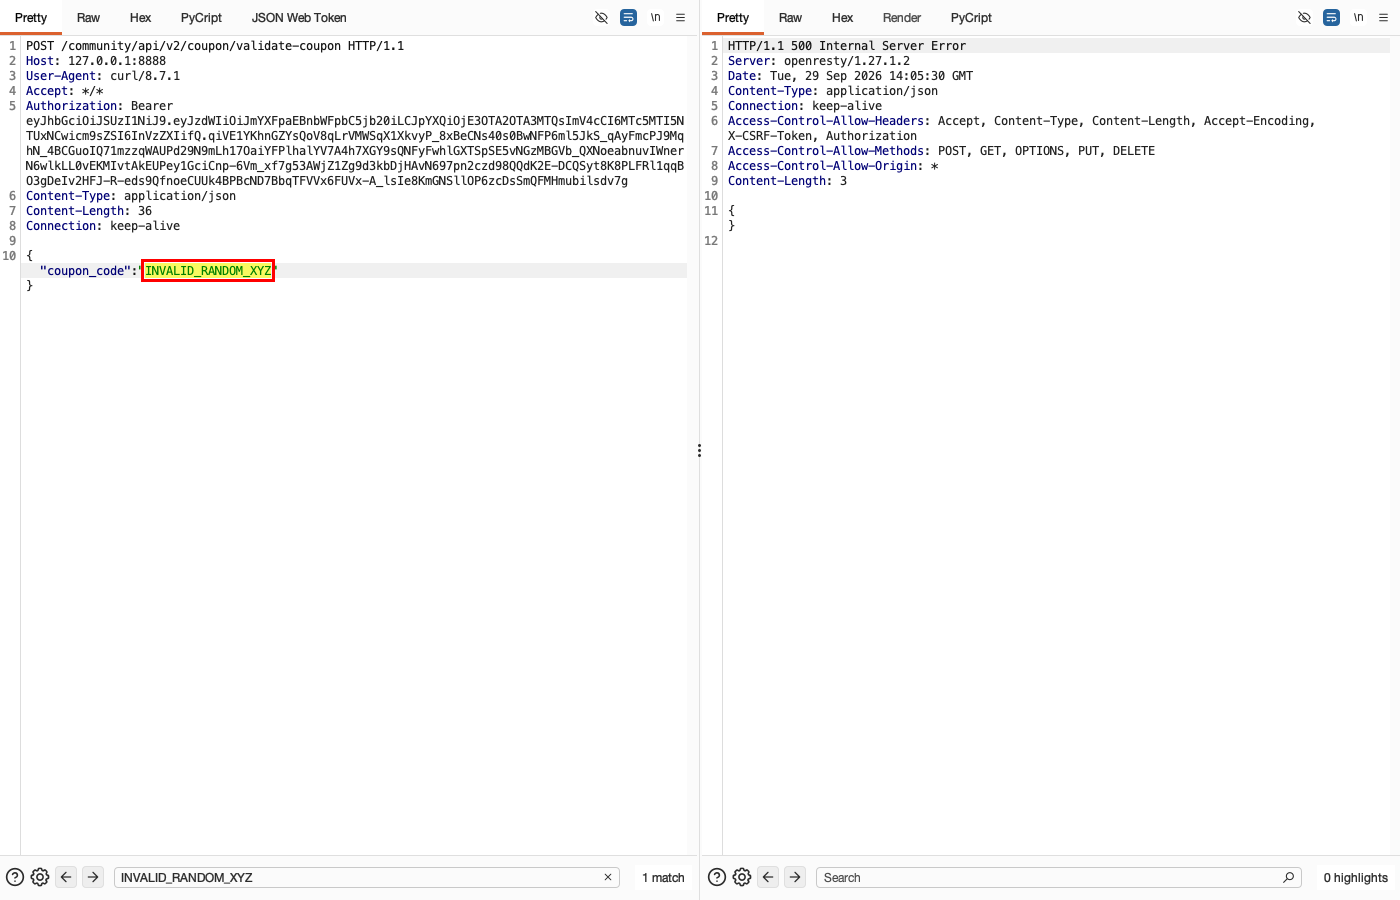
Normal: valid code TRAC075 -> 200. Test: unknown random string -> rejected. PASS (normal input validation holds). Operator injection is covered in [FAIL].
Endpoint
POST http://127.0.0.1:8888/community/api/v2/coupon/validate-coupon
Affected feature
Coupon Validation (crapi-community)
Remediation
Enforce the string type and reject operators/objects (see the related [FAIL] finding).
Proof of concept
- (Screenshot 1) NORMAL: coupon_code="TRAC075" (valid) -> 200.
- (Screenshot 2) TEST: coupon_code="INVALID_RANDOM_XYZ" (unknown string) -> rejected (normal validation holds).
The complete record
LAB All targets are lab systems. Nothing here is a client engagement. Evidence is shown as recorded; secrets are blacked out.
Normal: valid code accepted
Normal flow: a valid coupon code supplied as a string (TRAC075) returns 200.
HTTP request
POST /community/api/v2/coupon/validate-coupon HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]

{"coupon_code":"TRAC075"}
HTTP response
HTTP/1.1 200 OK
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 79

{
  "coupon_code": "TRAC075",
  "amount": "75",
  "CreatedAt": "2026-09-28T14:27:38.729Z"
}
Result: unrecognized string rejected (PASS)
Result (PASS): an unrecognized plain-string input is rejected. This result applies only to normal string input; injecting NoSQL operators still exposes the weakness described in [FAIL].
HTTP request
POST /community/api/v2/coupon/validate-coupon HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]

{"coupon_code":"INVALID_RANDOM_XYZ"}
HTTP response
HTTP/1.1 500 Internal Server Error
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 3

{}
← Previous case: NoSQL Injection - Community - Coupon Validation Next case: OTP Bruteforce Protection - Authentication - Password Reset (Per-Session Lockout) →