Vulnerability
[FAIL] Improper Inventory Management - Authentication - OTP Endpoint Versions
Description
The OTP verification endpoint exists in several versions that are active at the same time: the older /identity/api/auth/v2/check-otp still works alongside the current v3. Retired/undocumented versions enlarge the attack surface and may enforce different security controls.
Impact
Confidentiality & Integrity: the still-live legacy version widens the attack surface; an attacker can pick the version with the weakest protection (e.g. for OTP brute force).
CWE
CWE-1059: Insufficient Technical Documentation (related to CWE-1104: Use of Unmaintained Third Party Components / legacy versions)
OWASP
API9:2023 - Improper Inventory Management
Scenario
v3 (the current version) is active. Exploitation: v2 (the legacy version) is also still active -> improper inventory (the legacy version was never decommissioned).
Endpoint
POST http://127.0.0.1:8888/identity/api/auth/v2/check-otp
POST http://127.0.0.1:8888/identity/api/auth/v3/check-otp
Affected feature
Password Reset via OTP (crapi-identity)
Remediation
- Disable/retire legacy API versions (v2) that are no longer used.
- Maintain an API version inventory and document the active endpoints.
- Apply uniform security controls across every version still in service.
Proof of concept
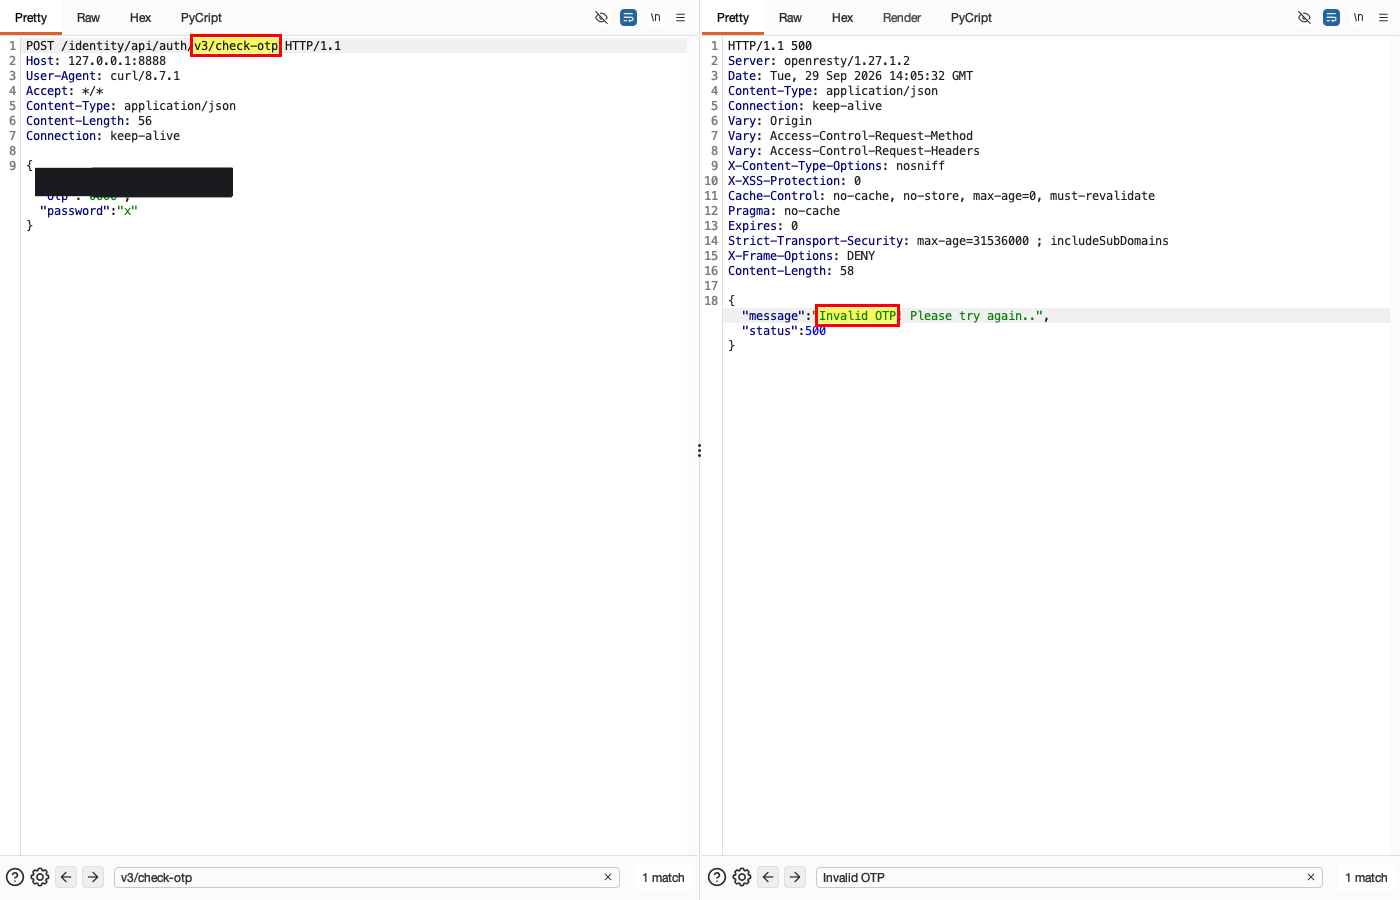
- (Screenshot 1) POST /identity/api/auth/v3/check-otp (current version) -> responds.
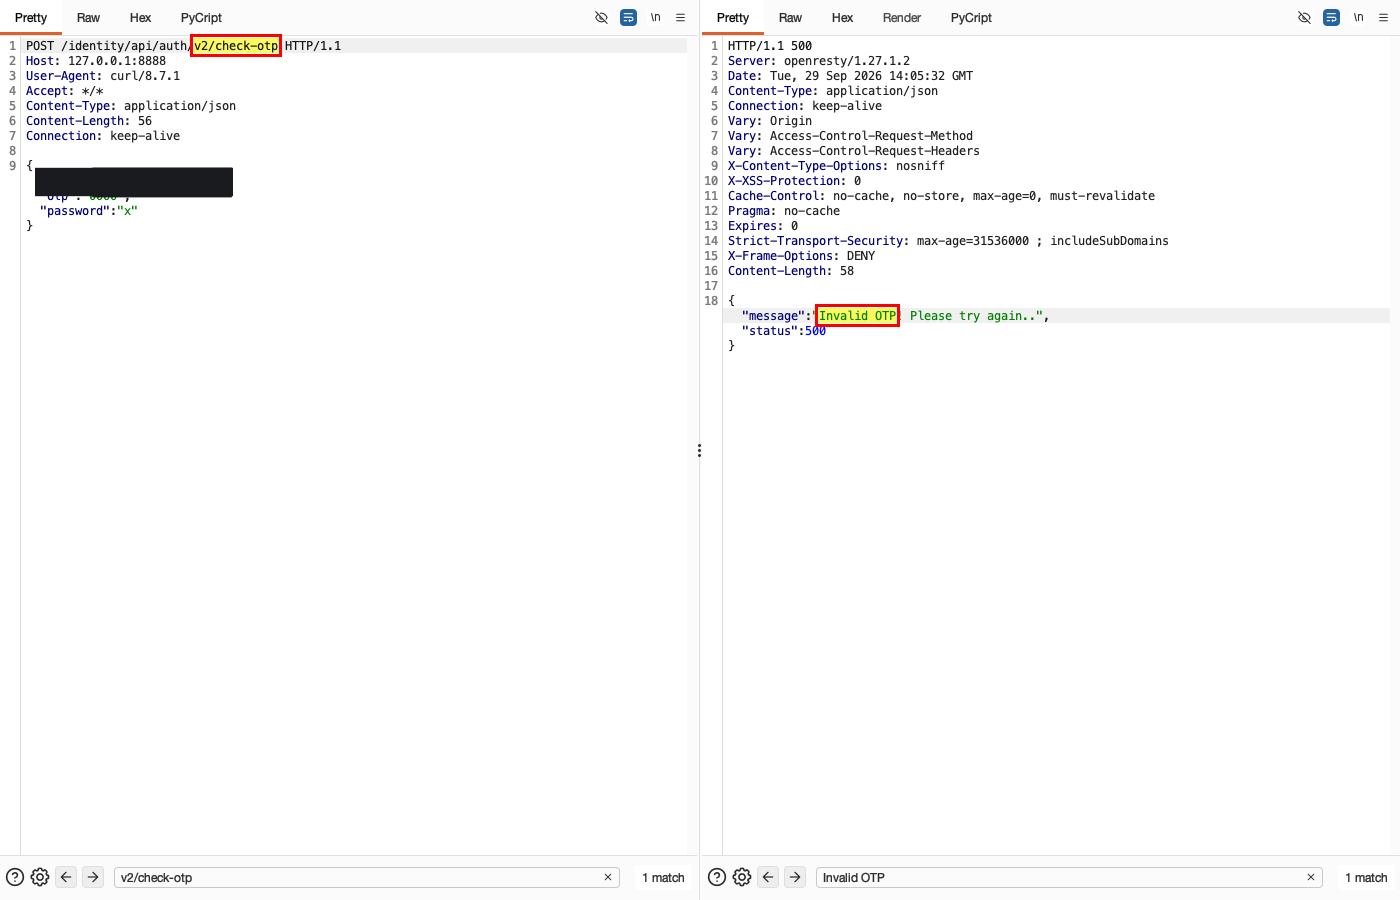
- (Screenshot 2) POST /identity/api/auth/v2/check-otp (LEGACY version) -> still responds (Invalid OTP), proving the legacy version has not been decommissioned.
The complete record
LAB All targets are lab systems. Nothing here is a client engagement. Evidence is shown as recorded; secrets are blacked out.
Current version: v3/check-otp
The latest version of the OTP verification endpoint (v3) is active.
HTTP request
POST /identity/api/auth/v3/check-otp HTTP/1.1
Host: 127.0.0.1:8888
Content-Type: application/json

{"email":"[REDACTED-EMAIL]","otp":"0000","password":"[REDACTED-LAB-VALUE]"}
HTTP response
HTTP/1.1 500
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 58

{
  "message": "Invalid OTP! Please try again..",
  "status": 500
}
Observation: older v2 remains active
Impact: the older v2/check-otp endpoint remains active alongside v3, expanding the attack surface. Its protections may differ from v3 or be weaker; this capture does not establish a bypass.
HTTP request
POST /identity/api/auth/v2/check-otp HTTP/1.1
Host: 127.0.0.1:8888
Content-Type: application/json

{"email":"[REDACTED-EMAIL]","otp":"0000","password":"[REDACTED-LAB-VALUE]"}
HTTP response
HTTP/1.1 500
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 58

{
  "message": "Invalid OTP! Please try again..",
  "status": 500
}
← Previous case: Broken Object Level Authorization - Workshop - Mechanic Report (Unauthenticated) Next case: JWT Signature Not Verified - Authentication - JWT Validation →