Vulnerability
[PASS] Broken Object Level Authorization - Workshop - Mechanic Report (Unauthenticated)
Description
Tested access to the mechanic_report endpoint without authentication.
Impact
No impact: the server requires authentication and rejects the request (401).
CWE
CWE-306: Missing Authentication for Critical Function (tested, not vulnerable on this path)
OWASP
API1:2023 - Broken Object Level Authorization (negative test - unauthenticated path)
Scenario
Normal: read a report with a token -> 200. Exploitation: remove the token -> 401. PASS (authentication control holds).
Endpoint
GET http://127.0.0.1:8888/workshop/api/mechanic/mechanic_report?report_id={id}
Affected feature
Mechanic Service Report (crapi-workshop)
Remediation
Keep the authentication requirement; add object ownership verification (see the related [FAIL] finding).
Proof of concept
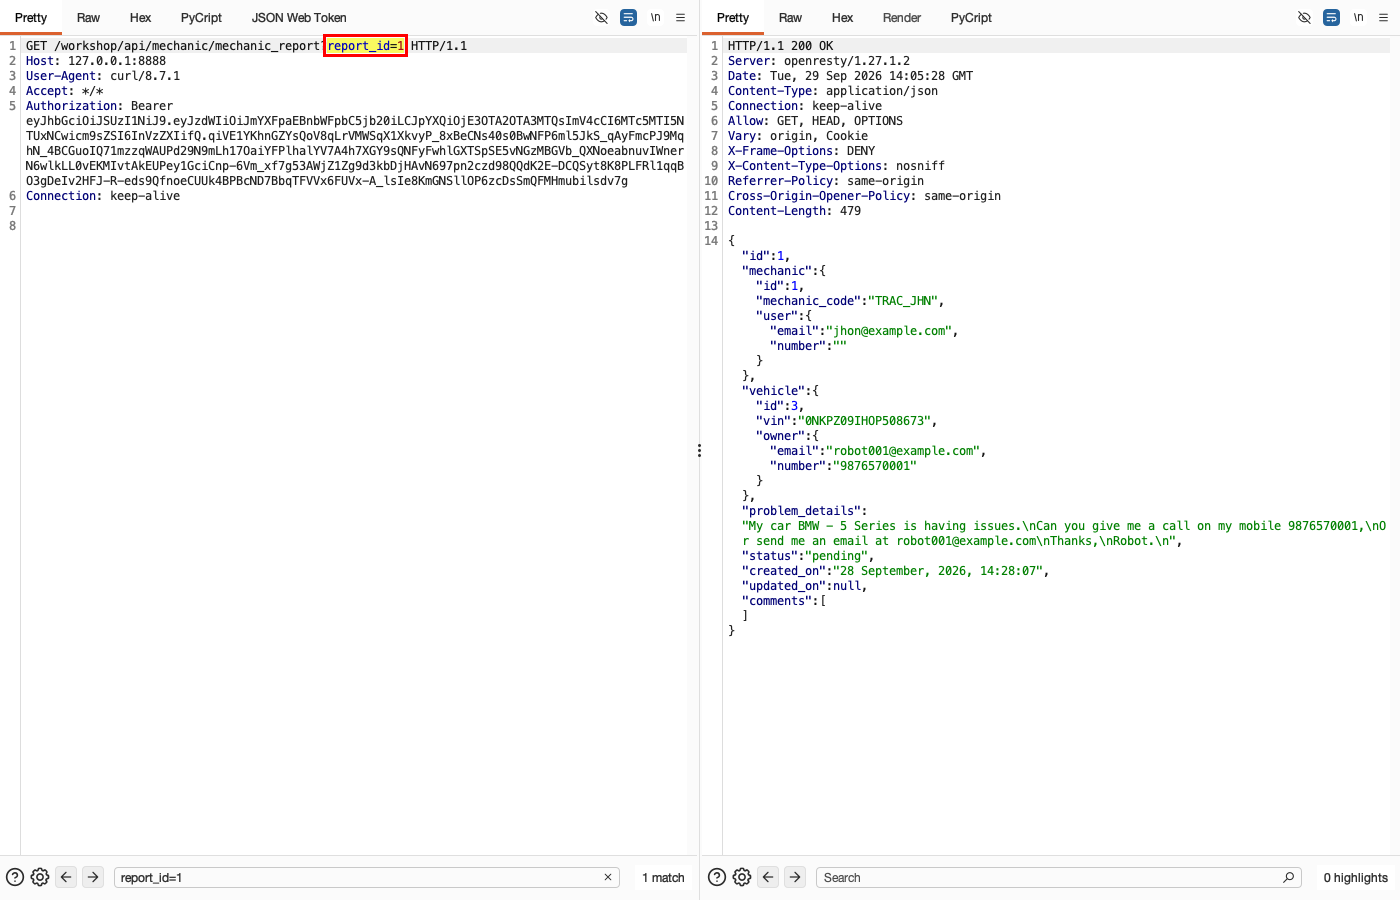
- (Screenshot 1) NORMAL: GET mechanic_report?report_id=1 with a token -> 200.
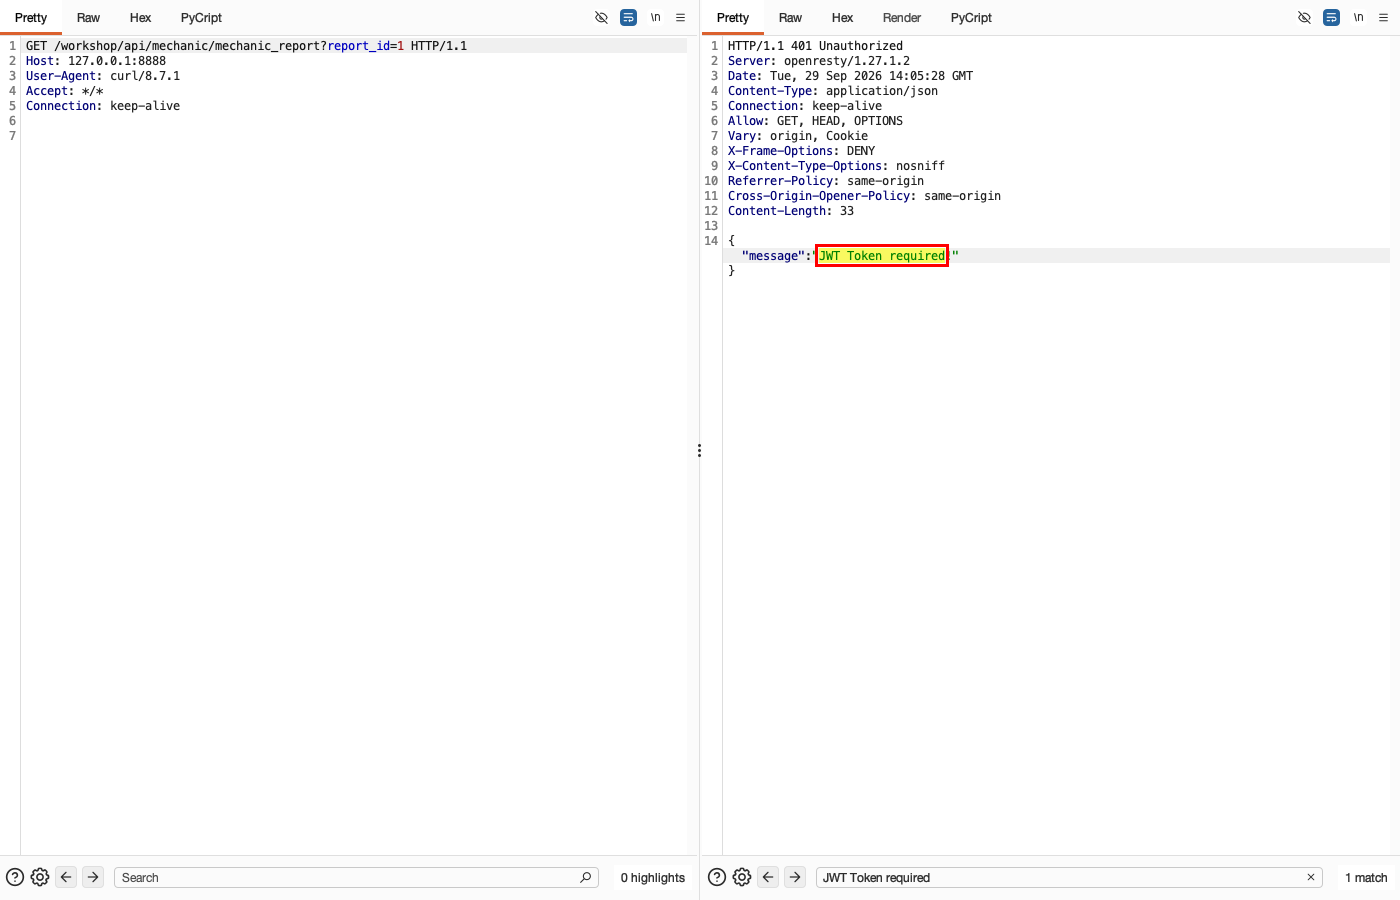
- (Screenshot 2) EXPLOITATION: resend WITHOUT the Authorization header -> 401 (authentication control holds).
The complete record
LAB All targets are lab systems. Nothing here is a client engagement. Evidence is shown as recorded; secrets are blacked out.
Normal: report with a token (authenticated)
Normal flow: reading the mechanic report with a valid token returns 200.
HTTP request
GET /workshop/api/mechanic/mechanic_report?report_id=1 HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]
HTTP response
HTTP/1.1 200 OK
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 479

{
  "id": 1,
  "mechanic": {
    "id": 1,
    "mechanic_code": "TRAC_JHN",
    "user": {
      "email": "[REDACTED-EMAIL]",
      "number": ""
    }
  },
  "vehicle": {
    "id": 3,
    "vin": "0NKPZ09IHOP508673",
    "owner": {
      "email": "[REDACTED-EMAIL]",
      "number": "9876570001"
    }
  },
  "problem_details": "My car BMW - 5 Series is having issues.\nCan you give me a call on my mobile 9876570001,\nOr send me an email at [REDACTED-EMAIL]\nThanks,\nRobot.\n",
  "status": "pending",
  "created_on": "28 September, 2026, 14:28:07",
  "updated_on": null,
  "comments": []
}
Result: report access without a token rejected (PASS)
Result (PASS): access without a token returns 401. Authentication held in this test, but BOLA is still possible with another user's token; see [FAIL].
HTTP request
GET /workshop/api/mechanic/mechanic_report?report_id=1 HTTP/1.1
Host: 127.0.0.1:8888
Accept: application/json

# HEADER Authorization SENGAJA DIHAPUS
HTTP response
HTTP/1.1 401 Unauthorized
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 33

{
  "message": "JWT Token required!"
}
← Previous case: Broken Object Level Authorization - Workshop - Mechanic Report Next case: Improper Inventory Management - Authentication - OTP Endpoint Versions →