Vulnerability
[PASS] Broken Object Level Authorization - Shop - Return Order
Description
Tested whether the order return action (return_order) is vulnerable to BOLA by attempting to return an order belonging to another user.
Impact
No impact: the server enforces ownership authorization and rejects the request (403).
CWE
CWE-639: Authorization Bypass Through User-Controlled Key (tested, not vulnerable)
OWASP
API1:2023 - Broken Object Level Authorization (negative test)
Scenario
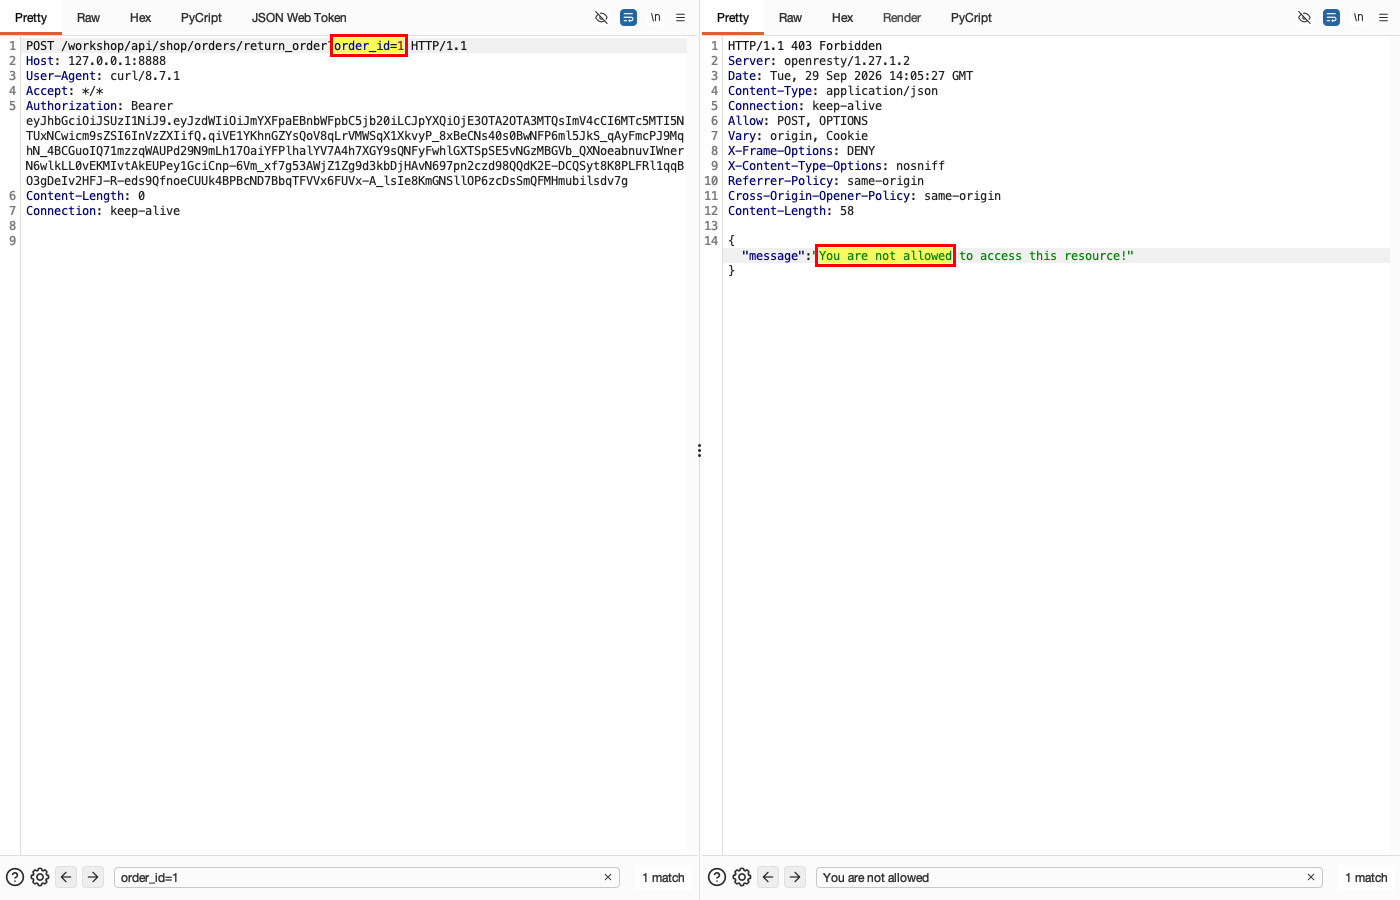
Exploitation: return_order?order_id=1 (not owned by the attacker) -> 403. PASS (control holds, CIA not violated).
Endpoint
POST http://127.0.0.1:8888/workshop/api/shop/orders/return_order?order_id={id}
Affected feature
Order Return (crapi-workshop)
Remediation
Keep the ownership check on the return action (the current state is correct).
Proof of concept
- (Screenshot 1) EXPLOITATION: POST return_order?order_id=1 (an order owned by another user) with the attacker token -> 403 "You are not allowed to access this resource!" (control holds).
The complete record
LAB All targets are lab systems. Nothing here is a client engagement. Evidence is shown as recorded; secrets are blacked out.
Result: another user's return rejected (PASS)
Result (PASS): an attempt to return another user's order (order_id=1) is rejected with 403. Object-level authorization held in this test; no impact on confidentiality, integrity or availability was observed.
HTTP request
POST /workshop/api/shop/orders/return_order?order_id=1 HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]
HTTP response
HTTP/1.1 403 Forbidden
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 58

{
  "message": "You are not allowed to access this resource!"
}
← Previous case: Broken Function Level Authorization - Workshop - Management Users Endpoint Next case: Broken Object Level Authorization - Vehicle - Location Tracking →