Vulnerability
[PASS] Broken Function Level Authorization - Admin - Administrative Endpoints
Description
The test attempted to call administrative functions directly with an ordinary user token, bypassing the admin panel interface. Tested endpoints included creating a new administrator, deleting accounts, and suspending accounts.
Impact
No impact. Control holds: all three administrative endpoints check the caller's role and reject ordinary user tokens with HTTP 403. Calling them directly without going through the interface grants no additional privileges.
Important note: this control is only as safe as the role claim in the token. Because the is_admin claim is read from the token and the token signature is not verified correctly, this role check can be bypassed with a forged token, as proven in the JWT Signature Not Verified finding.
CWE
CWE-285: Improper Authorization
OWASP
A01:2021 - Broken Access Control
Scenario
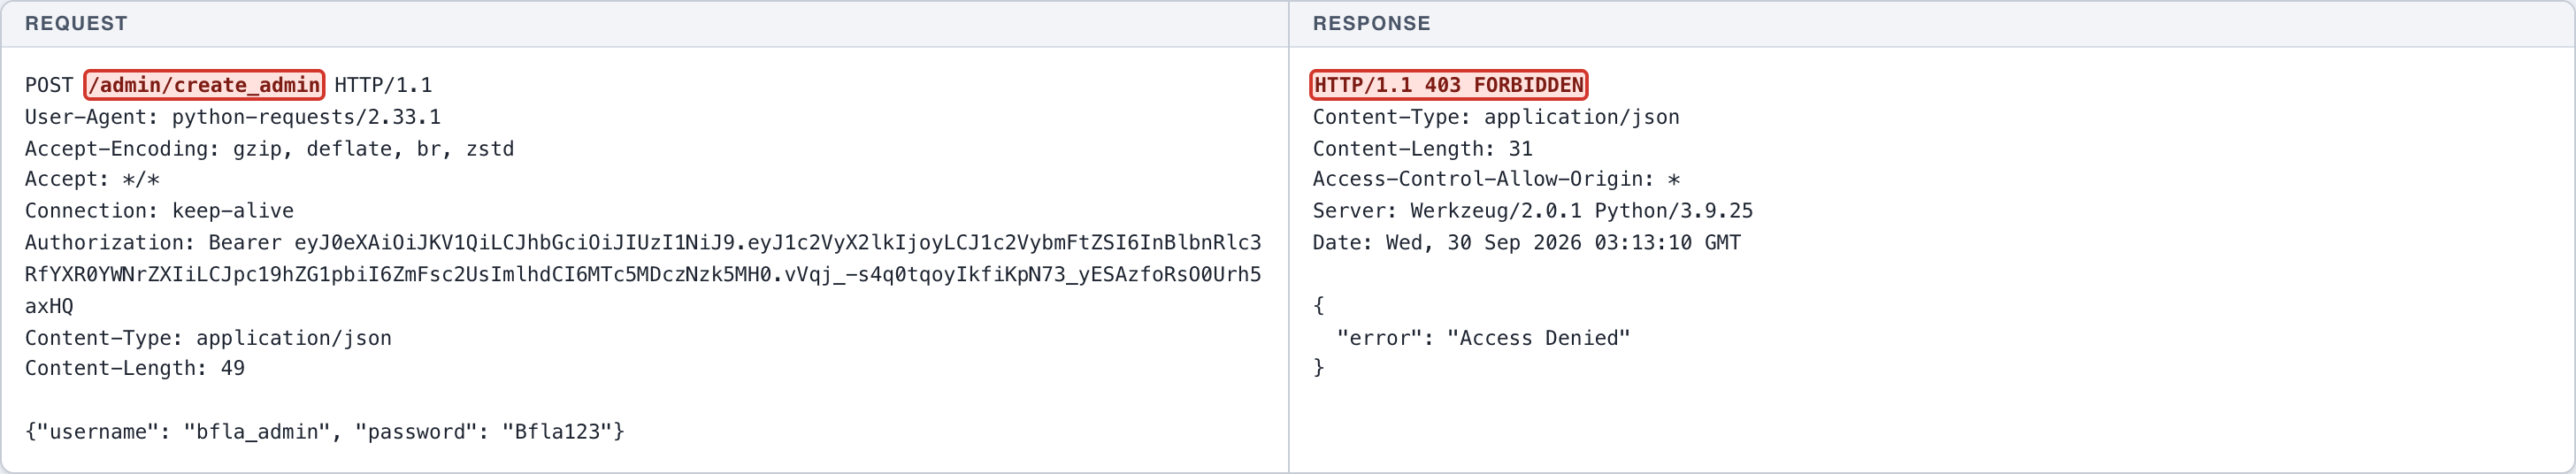
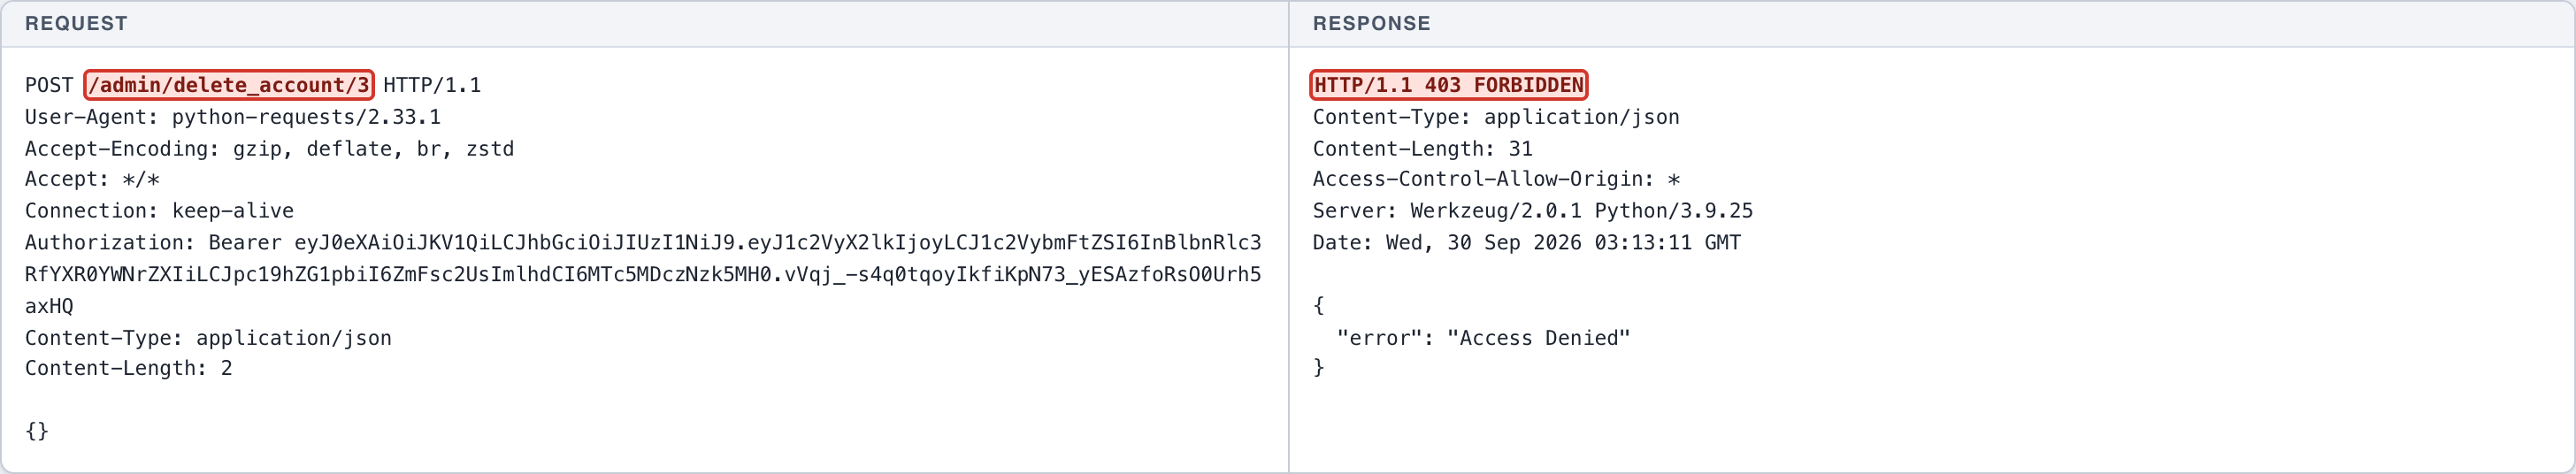
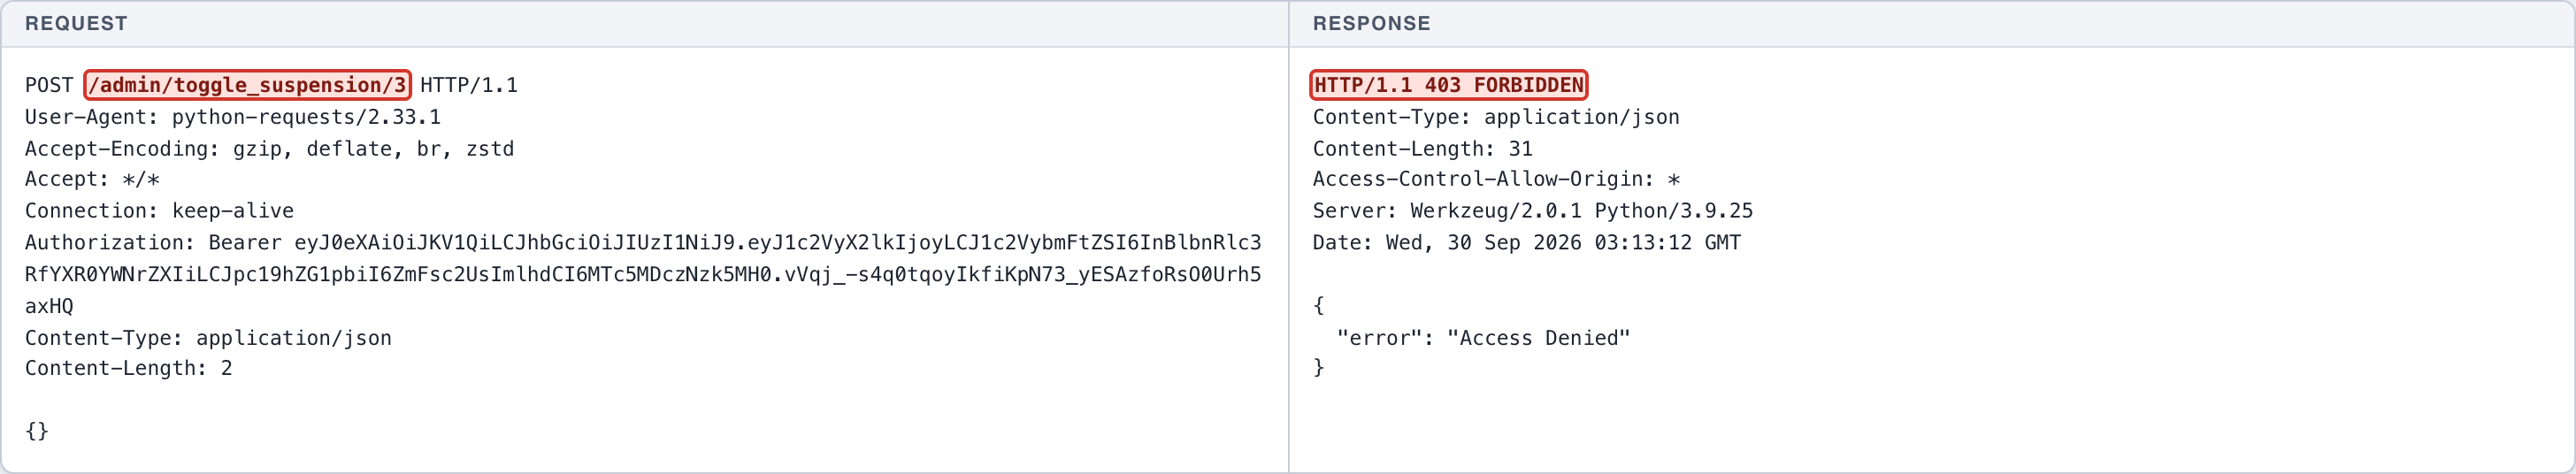
An ordinary user token was used to call /admin/create_admin, /admin/delete_account/3, and /admin/toggle_suspension/3 directly. Result: all were rejected with HTTP 403.
Endpoint
POST http://127.0.0.1:5001/admin/create_admin
POST http://127.0.0.1:5001/admin/delete_account/<user_id>
POST http://127.0.0.1:5001/admin/toggle_suspension/<user_id>
Affected feature
Administrative functions (create admin, delete account, suspend account)
Remediation
- Keep the role check on all administrative endpoints.
- Fetch the role from the database using the token subject rather than from a claim inside the token, so this control cannot be bypassed with a forged token.
Proof of concept
- (Screenshot 1) ATTEMPT: an ordinary user token calls /admin/create_admin -> HTTP 403, control holds.
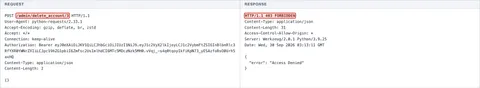
- (Screenshot 2) ATTEMPT: an ordinary user token calls /admin/delete_account/3 -> HTTP 403, control holds.
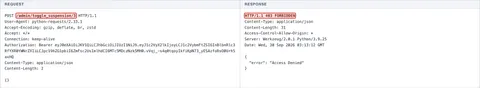
- (Screenshot 3) ATTEMPT: an ordinary user token calls /admin/toggle_suspension/3 -> HTTP 403, control holds.
The complete record
LAB All targets are lab systems. Nothing here is a client engagement. Evidence is shown as recorded; secrets are blacked out.
HTTP request
POST /admin/create_admin HTTP/1.1
User-Agent: python-requests/2.33.1
Accept-Encoding: gzip, deflate, br, zstd
Accept: */*
Connection: keep-alive
Authorization: Bearer [REDACTED-LAB-TOKEN]
Content-Type: application/json
Content-Length: 49

{"username": "bfla_admin", "password": "[REDACTED-LAB-VALUE]"}
HTTP response
HTTP/1.1 403 FORBIDDEN
Content-Type: application/json
Content-Length: 31
Access-Control-Allow-Origin: *
Server: Werkzeug/2.0.1 Python/3.9.25
Date: Wed, 30 Sep 2026 03:13:10 GMT

{
  "error": "Access Denied"
}
HTTP request
POST /admin/delete_account/3 HTTP/1.1
User-Agent: python-requests/2.33.1
Accept-Encoding: gzip, deflate, br, zstd
Accept: */*
Connection: keep-alive
Authorization: Bearer [REDACTED-LAB-TOKEN]
Content-Type: application/json
Content-Length: 2

{}
HTTP response
HTTP/1.1 403 FORBIDDEN
Content-Type: application/json
Content-Length: 31
Access-Control-Allow-Origin: *
Server: Werkzeug/2.0.1 Python/3.9.25
Date: Wed, 30 Sep 2026 03:13:11 GMT

{
  "error": "Access Denied"
}
HTTP request
POST /admin/toggle_suspension/3 HTTP/1.1
User-Agent: python-requests/2.33.1
Accept-Encoding: gzip, deflate, br, zstd
Accept: */*
Connection: keep-alive
Authorization: Bearer [REDACTED-LAB-TOKEN]
Content-Type: application/json
Content-Length: 2

{}
HTTP response
HTTP/1.1 403 FORBIDDEN
Content-Type: application/json
Content-Length: 31
Access-Control-Allow-Origin: *
Server: Werkzeug/2.0.1 Python/3.9.25
Date: Wed, 30 Sep 2026 03:13:12 GMT

{
  "error": "Access Denied"
}
← Previous case: Active Debug Code - Application Server - Werkzeug Debugger Next case: Broken Object Level Authorization - Accounts - Balance Lookup →