Vulnerability
[PASS] Mass Assignment - Authentication - User Registration
Description
Tested whether the registration endpoint is vulnerable to mass assignment by injecting privileged fields (role=admin, isAdmin=true) into the signup body.
Impact
No impact: the server ignores privileged fields, so no privilege escalation occurs.
CWE
CWE-915: Improperly Controlled Modification of Dynamically-Determined Object Attributes (tested, not vulnerable)
OWASP
API3:2023 - Broken Object Property Level Authorization (negative test)
Scenario
Normal: standard registration. Exploitation: signup + role=admin/isAdmin. Result: login shows the role remains user -> PASS (control holds, CIA not violated).
Endpoint
POST http://127.0.0.1:8888/identity/api/auth/signup
Affected feature
User Registration (crapi-identity)
Remediation
Keep the allow-list of fields the client may set during registration (the current state is correct).
Proof of concept
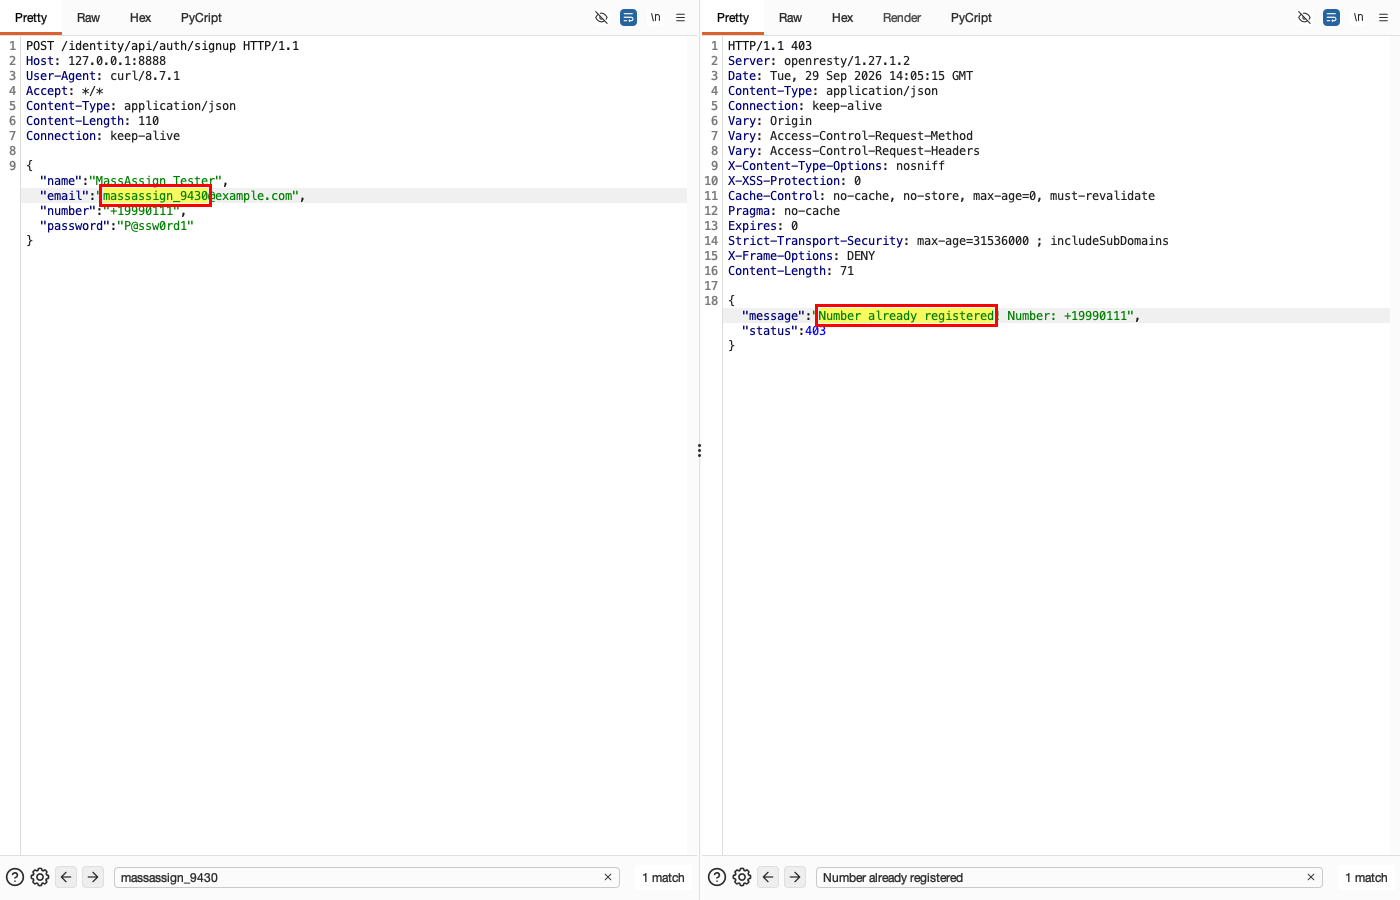
- (Screenshot 1) NORMAL: signup with standard fields -> 200.
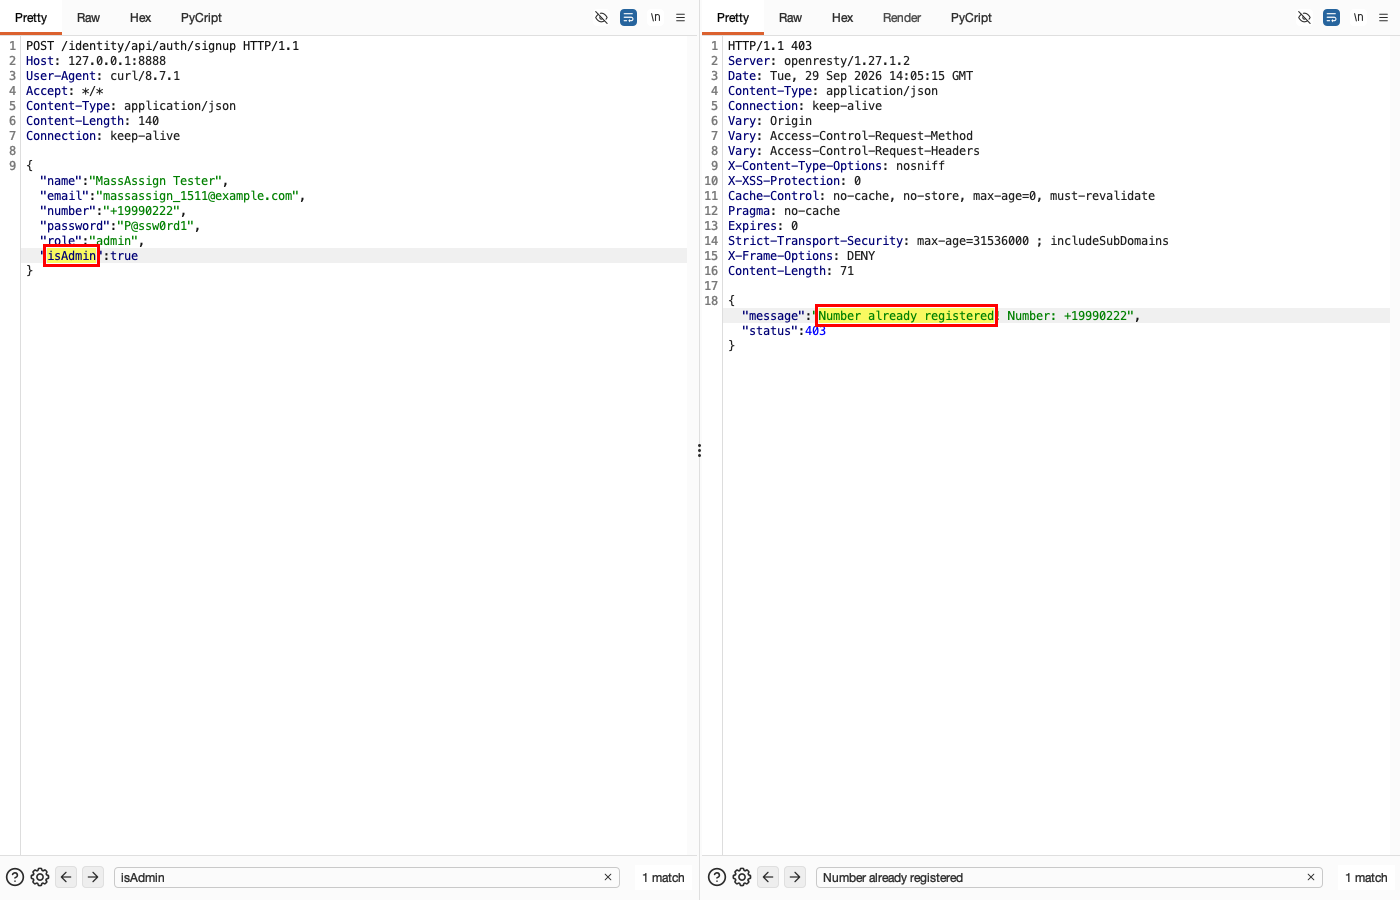
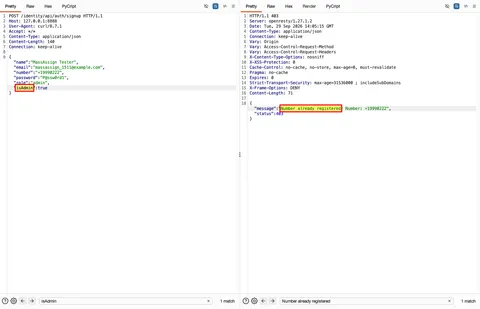
- (Screenshot 2) EXPLOITATION: signup with the addition of role=admin & isAdmin=true -> 200 (registered).
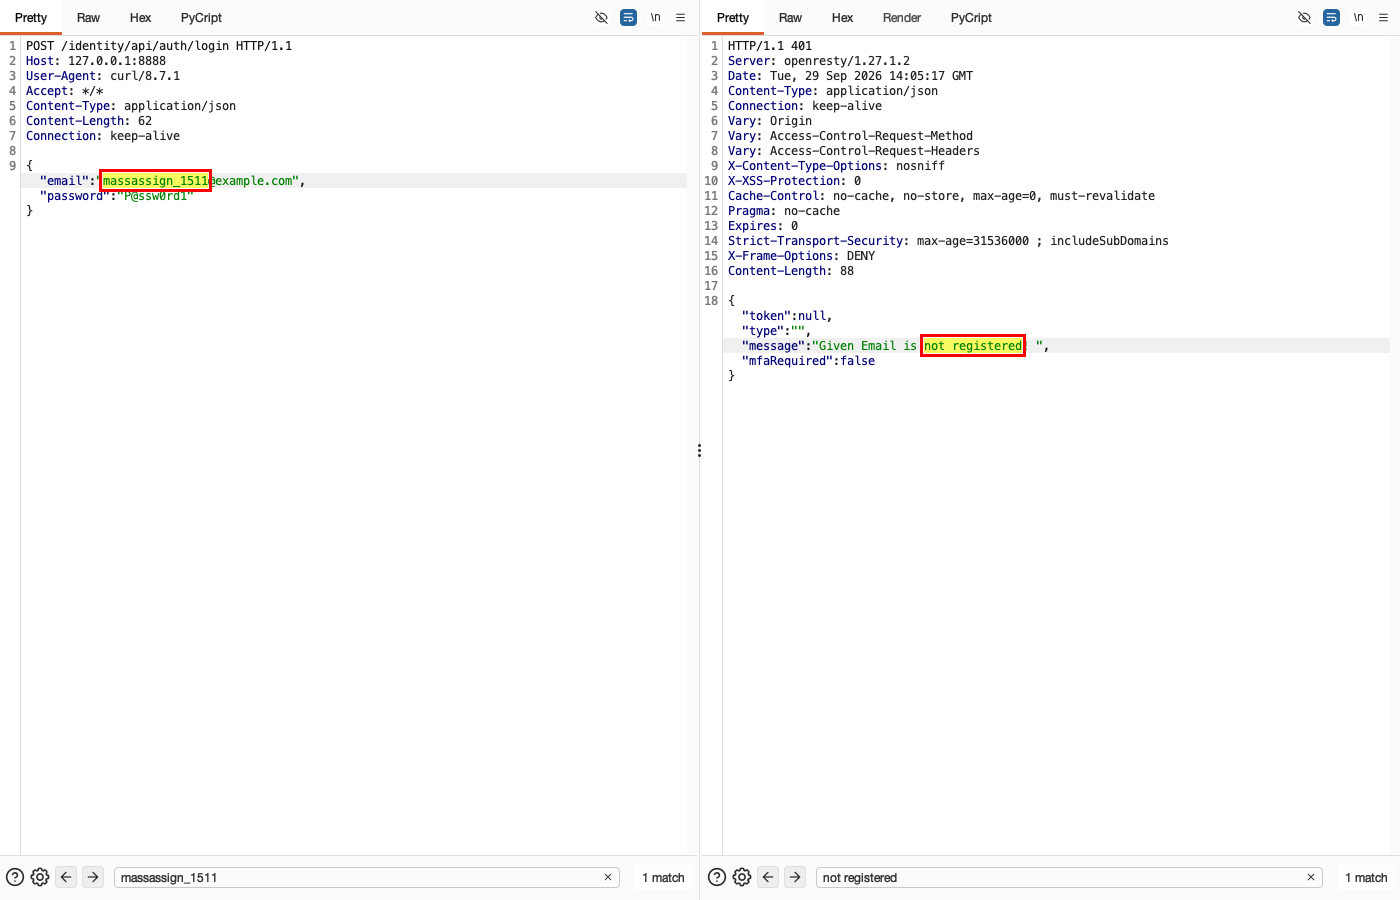
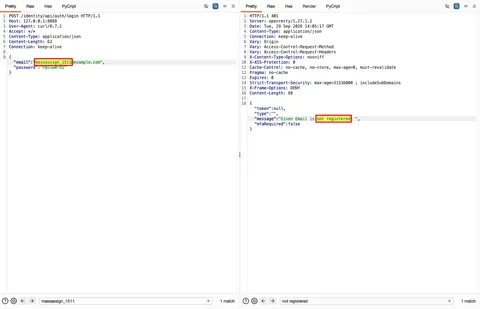
- (Screenshot 3) RESULT: log in to that account -> the JWT role remains "user" -> privileged fields were ignored (control holds).
The complete record
LAB All targets are lab systems. Nothing here is a client engagement. Evidence is shown as recorded; secrets are blacked out.
Normal: standard registration
Normal flow: registration using the standard fields, without the role field.
HTTP request
POST /identity/api/auth/signup HTTP/1.1
Host: 127.0.0.1:8888
Content-Type: application/json

{"name":"MassAssign Tester","email":"[REDACTED-EMAIL]","number":"+19990111","password":"[REDACTED-LAB-VALUE]"}
HTTP response
HTTP/1.1 403
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 71

{
  "message": "Number already registered! Number: +19990111",
  "status": 403
}
Attempt: add role=admin and isAdmin=true
Exploit attempt: add role=admin and isAdmin=true to the signup body to request elevated privileges.
HTTP request
POST /identity/api/auth/signup HTTP/1.1
Host: 127.0.0.1:8888
Content-Type: application/json

{"name":"MassAssign Tester","email":"[REDACTED-EMAIL]","number":"+19990222","password":"[REDACTED-LAB-VALUE]","role":"admin","isAdmin":true}
HTTP response
HTTP/1.1 403
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 71

{
  "message": "Number already registered! Number: +19990222",
  "status": 403
}
Result: privileged fields ignored (PASS)
Result (PASS): logging in to the new account shows role="user". The server ignored the privileged fields, so the exploit attempt failed. No impact on confidentiality, integrity or availability was observed in this test.
HTTP request
POST /identity/api/auth/login HTTP/1.1
Host: 127.0.0.1:8888
Content-Type: application/json

{"email":"[REDACTED-EMAIL]","password":"[REDACTED-LAB-VALUE]"}
HTTP response
HTTP/1.1 401
Server: openresty/1.27.1.2
Content-Type: application/json
Content-Length: 88

{
  "token": null,
  "type": "",
  "message": "Given Email is not registered! ",
  "mfaRequired": false
}

# JWT payload -> role: "user"  (BUKAN admin)
← Previous case: JWT Signature Not Verified - Authentication - JWT Validation Next case: NoSQL Injection - Community - Coupon Validation →